PROCESSING...

Anti-Money Laundering
Consulting Services & Strategies

0 Items - Total: $0.00 CAD

Canada’s Proposed AML Changes for MSBs

What’s Old is New Again, Well Updated

On June 9th, 2018, draft amendments to the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) and its enacted regulations (there are five separate regulations that we’re going to collectively call regulations here for simplicity’s sake). This article is intended to give a high-level summary of the proposed amendments as they relate to Money Services Businesses (MSBs).

This article should not be considered advice (legal, tax or otherwise). That said, any of the content shared here may be used and shared freely – you don’t need our permission. While we’d love for content that we’ve written to be attributed to us, we believe that it’s more important to get reliable information into the hands of community members (meaning that if you punk content that we wrote, we may think you’re a jerk but we’re not sending an army of lawyers).

Finally, we want to encourage the community to discuss the proposed changes and submit meaningful feedback for policy makers. The comment period for this draft is 90 days. After this, the Department of Finance takes the feedback to the bat cave and drafts a final version of the amendments. From the time that the final version is published, the draft indicates that there will be 12 months of transition to comply with the new requirements.

♬The Times Regulations Are Changing♬

Foreign MSBs

Currently, the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) has issued a policy interpretation (PI-5594) in August of 2013, which states that a “real and substantial connection” to Canada must be present for an entity to be required to register as an MSB with FINTRAC.  A “real and substantial connection” was defined in the interpretation as having one or more of the following:

  • Whether the business is incorporated in Canada;
  • Whether the business has agents in Canada;
  • Whether the business has physical locations in Canada; and/ or
  • Whether the business maintains a bank account or a server in Canada.

The draft amendments introduce a new definition, which is “Foreign Money Services Business” that means anyone serving Canadian customers or entities in Canada is now subject to all Canadian requirements no matter where they are located.  Throughout the proposed changes, where there is a reference to money services businesses, there is also a reference to foreign money services businesses.  This will be significant to MSBs who operate non-face-to-face in the online marketplace and do not reside in Canada.

Non-Face-To-Face Customer Identification

Currently, there is a requirement that when customers are identified using the dual process method, the document and/or data that you collect is in its “original” format. This has been interpreted to mean that if the customer receives a utility bill in the mail, they must send you the original paper (not scanned or copied) document. The word “original” will be replaced with “authentic” (meaning that so long as you believe that the utility bill is a real utility bill for that person, it doesn’t need to be the same piece of paper that they received in the mail).

In addition, there are provisions that would allow reporting entities to rely on the identification conducted previously by other reporting entities. If this method is used to identify a customer, the reporting entity must immediately obtain the identification information from the other reporting entity and have a written agreement in place requiring the entity doing the identification to provide the identification verification within 3 days of the request.

Reporting EFTs of $10,000 or More

If you conduct international remittance transactions at the request of your customers, the requirement to report transactions of $10,000 or more will now be your responsibility, not your financial services provider.

The proposed change removes the language commonly known as the “first in, last out” rule.  This means that the first person/entity to ‘touch’ the funds for transactions incoming to Canada or the last person/entity to ‘touch’ the funds for a transaction outgoing from Canada had the reporting obligation (as long as the prescribed information was provided to them).

The update will change the reporting obligation to whoever maintains the customer relationship. So if you initiate a transaction at your customer’s request (outgoing transaction) or provide final receipt of payment to your customer (incoming transaction), it will be your obligation to report that transaction to FINTRAC.

For example, if the flow of the instructions for payment were as follows:

Currently, the reporting obligation of the outgoing EFT would fall to the bank in Canada.  With the draft updates, the reporting obligation would now fall to the MSB in Canada, because they have the relationship with the customer initiating the transaction.


Third Party Determination

Currently, the obligation to determine whether a third party is involved in a transaction relates to Large Cash Transactions.  The proposed changes would include the obligation to make a third party determination for all EFTs of $10,000 or more.  This would also require similar record keeping obligations as a third party determination under the current Large Cash Transaction records.

Suspicious Transaction Reporting

Currently, if a reporting entity has reasonable grounds to suspect that a transaction or attempted transaction is related to money laundering or terrorist financing, a report must be submitted to FINTRAC within 30 days of the date that a fact was discovered that caused the suspicion. This change appeared in the last round of amendments that came into force last year, and the proposed new wording would be another significant change:

The person or entity shall send the report to the Centre within three days after the day on which measures taken by them enable them to establish that there are reasonable grounds to suspect that the transaction or attempted transaction is related to the commission of a money laundering offence or a terrorist activity financing offence.

This means that a report would be due three days after the reporting entity conducts an investigation or does something that allows them to reach the conclusion that there are reasonable grounds to suspect.

Information Included In Reports to FINTRAC

Certain information is required in reports to FINTRAC. Even where information is marked as being optional, if a reporting entity has the information, it becomes mandatory to include it. Some of the additional proposed data fields are:

  • every reference number that is connected to the transaction,
  • type of device used by person who makes request online,
  • number that identifies device,
  • internet protocol address (IP address) used by device,
  • person’s user name, and
  • date and time of person’s online session in which request is made.

These fields may require significantly more data to be included in reports, especially for transactions that are conducted online.

Ongoing Compliance Training

Currently, there are five required elements of a Canadian AML compliance program, but there is soon to be a sixth.  Before you get too worried, it’s not that major.  The change is specific to your ongoing compliance training obligations, which says you must institute and document a plan for your ongoing compliance training program and the delivery of the training.  Basically, in your AML compliance program documentation, you need to provide a description of your training program for at least the next year and how the training will be delivered. Many MSBs have already implemented this best practice.

Risk Assessment Obligations

With the recent addition of the “New Technologies and Developments” category to the Risk-Based Approach requirements, the next logical progression has be added.  The updates include the obligation to assess the money laundering and terrorist financing risk of any new technology before implementation.  Meaning, if you are looking to take your business online and are going to use this fancy, new non-face-to-face ID system, you had better take careful inventory of where your risks are and be sure the appropriate controls have been put in place before going live. Much like the training plan, many MSBs have already implemented this best practice.

Virtual Currency

The draft updates also include major changes related to virtual currency. “Dealers in virtual currencies’ would be regulated as MSBs. New record keeping and reporting obligations would apply to all reporting entities that accept payment in virtual currency, or send virtual currency on behalf of their customers.

For more information on updates specific to virtual currency, please check out our full article.

What Next

If you’ve read this far, congratulations and thank you!

We hope that you will contribute your thoughts and comments. You can do this by contacting the Department of Finance directly. Their representative on this file is:

Lynn Hemmings

Acting Director General

Financial Systems Division

Financial Sector Policy Branch

Department of Finance

90 Elgin Street

Ottawa, Ontario

K1A 0G5

Email: fin.fc-cf.fin@canada.ca

If you would like assistance drafting a submission, or have questions that you would like Outlier to answer, please get in touch!

If you are interested in sharing your comments with the Canadian MSB Association (and we highly encourage you to do so) please email luisa@global-currency.com. She will have more information on the industry group’s submission and consultation process.
Canada’s AML Rules for “Virtual Currency”

On June 9th, 2018, draft amendments to the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) and its enacted regulations (there are five separate regulations, that we’re going to collectively call regulations here for simplicity’s sake). While not all of the proposed amendments are related to virtual currency, many are (the term virtual currency comes up 304 times in about 200 pages). This article is intended to give a high-level summary of the proposed amendments as they relate to virtual currency for businesses in that industry (exchanges, brokerages, etc.).

This article should not be considered advice (legal, tax or otherwise). That said, any of the content shared here may be used and shared freely – you don’t need our permission. While we’d love for content that we’ve written to be attributed to us, we believe that it’s more important to get reliable information into the hands of community members (meaning that if you punk content that we wrote, we may think you’re a jerk but we’re not sending an army of lawyers).

Finally, we want to encourage the community to discuss the draft and submit meaningful feedback for policymakers. To this end, we’re going to be posting, hosting and attending community events. We’ve also set up a survey that can be completed without submitting any personal information (though you may choose to do so). If you would like one of our compliance nerds at your event, please get in touch. If you’re already having a related event that benefits the community, let us know or post it in the comments.

The comment period for this draft is 90 days. After this, the Department of Finance takes the feedback to the bat cave and drafts a final version of the amendments. From the time that the final version is published, the draft indicates that there will be 12 months of transition to comply with the new requirements.

What to expect when you’re expecting (to be regulated)?

While we acknowledge that our sample is biased (people that talk to compliance geeks), we know that many businesses such as brokerages and exchanges have expected to be regulated as money services businesses (MSBs) since Bill C-31 was passed in 2014. Many of these businesses already have in place the required elements of an anti-money laundering (AML) compliance regime, including:

  1. The appointment of a Compliance Officer;
  2. Written policies and procedures;
  3. A documented risk assessment;
  4. Training; and
  5. Effectiveness testing (like an audit, but for compliance).

In addition, many have been voluntarily reporting suspicious activity to the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC), the body under which they expect to be regulated for AML.

The proposed amendments would formalize compliance program requirements, as well as create new requirements specific to businesses “dealing in virtual currency” (which would now be considered MSBs). While “dealing in virtual currency” itself is not defined, the text of the regulations implies that it will include exchanging, sending, and receiving virtual currency on behalf of other people or entities. Such entities would be required to register as MSBs if they are serving Canadian customers (whether or not they are located in Canada).

There are a number of thresholds that are proposed, including identification (at CAD 1,000) and reporting (at CAD 10,000). In each case, specific information must be collected and recorded. The identification methods that are available in these circumstances are relatively prescriptive, although the proposed amendments do make some headway towards supporting a broader array of identification methods by requiring that documents be considered “authentic” rather than requiring documents in their original format. Of course, as with any complex issue, guidance from FINTRAC will be required before we’re certain how this will be interpreted by the regulator (It’s good news; we’re just not sure how good, yet).

As always in compliance, the devil is in the details. What follows is a few of those key details, as well as some of the issues that we anticipate. We encourage you to conduct your own analysis and to join the conversation.

What’s In A Definition?

Definitions are generally not very interesting. When was the last time that you read the dictionary? (Sidenote: if you are a serious scrabble geek and do this on the regular, you will enjoy this section more than most)… In this case though, definitions matter. Definitions will make a difference in terms of the businesses and activities that are regulated, and how they are regulated. Fortunately, our community includes a number of engineers, debaters, and other individuals with a penchant for the precise – and your skills are needed here. We encourage you to carefully consider the following and to submit feedback on how they can be improved.

authorized user means a person who is authorized by a holder of a prepaid payment product account to have electronic access to funds or virtual currency available in the account by means of a prepaid payment product that is connected to it.

funds means

(a) cash and other fiat currencies, and securities, negotiable instruments or other financial instruments that indicate a title or right to or interest in them; or

(b) information that enables a person or entity to have access to a fiat currency other than cash.

For greater certainty, it does not include virtual currency. (fonds)

fiat currency means a currency that is issued by a country and is designated as legal tender in that country.

large virtual currency transaction record means a record that indicates the receipt of an amount of $10,000 or more in virtual currency in a single transaction and that contains the following information:

(a) the date of the receipt;

(b) if the amount is received for deposit into an account, the name of each account holder;

(c) the name, address and telephone number of every other person or entity that is involved in the transaction, the nature of their principal business or their occupation and, in the case of a person, their date of birth;

(d) the type and amount of each virtual currency involved in the receipt;

(e) the exchange rate used and the source of the exchange rate;

(f) the number of every other account that is affected by the transaction, the type of account and the name of each account holder;

(g) every reference number that is connected to the transaction;

(h) every other known detail that identifies the receipt; and

(i) if the amount is received by a dealer in precious metals and precious stones for the sale of precious metals, precious stones or jewellery,

(i) the type of precious metals, precious stones or jewellery,

(ii) the value of the precious metals, precious stones or jewellery, if different from the amount of virtual currency received, and

(iii) the wholesale value of the precious metals, precious stones or jewellery.

prepaid payment product means a product that is issued by a financial entity and that enables a person or entity to engage in a transaction by giving them electronic access to funds or virtual currency paid to a prepaid payment product account held with the financial entity in advance of the transaction. It excludes a product that enables a person or entity to access a credit or debit account or one that is issued for use only with particular merchants.

prepaid payment product account means an account that is connected to a prepaid payment product and that permits

(a) one or more transactions that total $1,000 or more to be conducted within a 24-hour period; or

(b) a balance of funds or virtual currency available of $1,000 or more to be maintained.

virtual currency means

(a) a digital currency that is not a fiat currency and that can be readily exchanged for funds or for another virtual currency that can be readily exchanged for funds; or

(b) information that enables a person or entity to have access to a digital currency referred to in paragraph (a).

virtual currency exchange transaction means an exchange, at the request of another person or entity, of virtual currency for funds, funds for virtual currency or one virtual currency for another.

virtual currency exchange transaction ticket means a record respecting a virtual currency exchange transaction — including an entry in a transaction register — that sets out

(a) the date of the transaction;

(b) in the case of a transaction of $1,000 or more, the name, address and telephone number of the person or entity that requests the exchange, the nature of their principal business or their occupation and, in the case of a person, their date of birth;

(c) the type and amount of each of the funds and virtual currencies involved in the payment made and received by the person or entity that requests the exchange;

(d) the method by which the payment is made and received;

(e) the exchange rate used and the source of the exchange rate;

(f) the number of every account that is affected by the transaction, the type of account and the name of each account holder;

(g) every reference number that is connected to the transaction; and

(h) every other known detail that identifies the transaction.

Diving Deeper – Obligations and Potential Issues

1 – Do the definitions capture unintended parties?

We were surprised to see that there were not specific carve-outs for certain types of tokens, including securities, and tokens intended specifically for gaming. The definition, as it’s currently written seems capable of encompassing both tokenized security offerings and gaming tokens.

In addition, the second part of the definition that includes “information that enables a person or entity to have access to a digital currency referred to in paragraph (a).” has the potential to open the definition even more broadly. For instance, if I have stored a copy of a seed phrase or a hardware device with a vault service – have they received virtual currency? Are they sending virtual currency to me if the contents of my vault are couriered to me?

 2 – What about peer-to-peer, decentralized applications, and smart contracts?

The amendments as they are presented appear to take the view that transactions have intermediaries. There are no specific carve-outs for peer-to-peer transactions (though we expect that previous guidance could be applied here), decentralized applications, and smart contracts. This may be a particularly contentious issue in the case of an exchange from one “virtual currency” to another – especially where such an exchange is initiated or completed without any human intervention. Similarly, questions arise for wallet service providers. For instance, what if a wallet provider does not have access to private keys, but connects to applications that permit users to initiate transactions that would be considered to be exchange transactions under the current definition?

That said, there are some astute exclusions, including the following activities which are explicitly not covered:

(a) a transfer or receipt of virtual currency as compensation for the validation of a transaction that is recorded in a distributed ledger; or

(b) an exchange, transfer or receipt of a nominal amount of virtual currency for the sole purpose of validating another transaction or a transfer of information.

Nonetheless, it is difficult to determine where the policymakers intended to draw the line, and where the regulator will later enforce it…

3 – Jurisdiction doesn’t matter; foreign money services businesses (MSBs) are covered.

While not specific to virtual currency, it is noteworthy that the proposed amendments expand the definition of an MSB to include any business that is providing prescribed services in Canada. As we’ve seen in the case of the NY BitLicense, badly drafted legislation can drive away business and lead to a lack of service providers willing to do business in a region.

While we’re not suggesting that the proposed amendments are nearly as ill-conceived as the NY BitLicense, it is important to consider whether or not these will affect Canadians’ ability to access services, and the attractiveness of the Canadian market generally for innovative international businesses. While we do not expect this particular amendment to be altered, we would encourage businesses located outside of Canada that serve Canadians to comment.

What Next?

If you’ve read this far, congratulations and thank you!

We hope that you will contribute your thoughts and comments. You can do this by contacting the Department of Finance directly. Their representative on this file is:

Lynn Hemmings

Acting Director General

Financial Systems Division

Financial Sector Policy Branch

Department of Finance

90 Elgin Street

Ottawa, Ontario

K1A 0G5

Email: fin.fc-cf.fin@canada.ca

If you would like assistance drafting a submission, or have questions that you would like Outlier to answer, please get in touch!

You can also answer specific questions in our survey, or join us at a community event.

Sanctions This Week: June 27th – July 1st, 2016

Sanctions Pic

OSFI

On June 27th, 2016, the Office of the Superintendent of Financial Institutions (OSFI) released two updates to the United Nations Security Council’s (UNSC’s) Al-Qaida and Taliban regulations sanctions list, amending 8 individuals and 1 entity.

The individuals are subject to the assets freeze, travel ban and arms embargo set out in paragraph 2 of Security Council resolution 2253 (2015) adopted under Chapter VII of the Charter of the United Nations.

All of the individuals are of different nationalities, but all have connections to Al-Qaida and French terrorist groups.  Some of the individuals have been detained and are currently serving out sentences.  Where others have arrest warrants issued by France, which are currently outstanding.

Go to the OSFI UNAQTR update on the OSFI page.

Go to the OSFI lists page.

OFAC

The U.S. Department of Treasury’s Branch, The Office of Foreign Asset Control (OFAC), released three updates last week.  One update was related to the Counter Terrorist Designations list.  The second update was the publication of new Panama-related and Kingpin Act General Licenses and related Frequently Asked Questions (FAQ). The FAQ update is related to recent adjustments made to the sanctions placed on Panama.

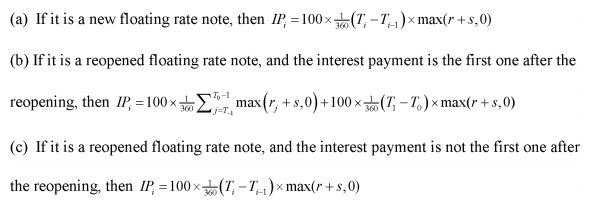
OFAC also released the details about the implementation of the Federal Civil Penalties Inflation Adjustment Act, where penalties related to AML failings have increased 150%, the allowable maximum.  The adjustment to the base fine of USD 11,000, has now increased to USD 27,500.  This is based off the Consumer Price Index, and if you are curious about the actual math, see the image below:

OFAC CMP Calculation

OFAC administers and enforces economic and trade sanctions based on U.S. foreign policy and national security goals.  The sanctions target countries, regimes, terrorists, international narcotics traffickers, the proliferation of weapons of mass destruction, and other threats to the national security, foreign policy or economy of the U.S.  The changes to the Counter Terrorism Designations list included the removal of 11 Somali and Djibouti nationals.  The update also included the addition of one individual of Indian nationality with ties to the entity added, which is a section of Al-Qaida operating within India.

See the Counter Terrorism Designations List update on OFAC’s website.

See the Kingpin Act/Panama-related General Licenses and FAQs update on OFAC’s website.

See the Implementation of the Federal Civil Penalties Inflation Adjustment Act update on OFAC’s website.

See OFAC’s Recent Actions page.

Need A Hand?

We would love to hear from you.  If there are subjects in this post that you would like to know more about, or if you need assistance with your compliance program, please contact us.

Sanctions This Week: May 30th-June 5th, 2016


OSFISanctions Pic

There were no updates released from OSFI this week.

Go to the OSFI lists page.

OFAC

The U.S. Department of Treasury’s Branch, The Office of Foreign Asset Control (OFAC), released two updates to five sanction lists last week.  The lists that were updated, include the following:

  • Burundi Sanctions Designations;
  • Kingpin Act Designations;
  • Kingpin Act/Panama-related General License; and
  • A Statement on the Felix Maduro Group.

OFAC administers and enforces economic and trade sanctions based on U.S. foreign policy and national security goals.  The sanctions target countries, regimes, terrorists, international narcotics traffickers, the proliferation of weapons of mass destruction, and other threats to the national security, foreign policy or economy of the U.S.

The Burundi Sanctions Designations update included three military individuals, who were added.  These individuals are all high ranking military officers who are currently serving.

The Kingpin Act Designations update, included the removal of a single Panamanian entity.  No details were provided about the reasoning for the removal.

The Kingpin Act/Panama-related General License update, covered the maintenance of certain operations within the country.  Much like the previous related updated, the information provided details how to deal with listed Panamanian individuals and entities included in the General Licenses.  However, this iteration referred to the maintenance of La Estrella and El Siglo Newspapers.

The statement on the Felix Maduro Group, is related to OFAC’s designation of Waked Money Laundering Organization and their shared ownership.  However, based on consultations with, and actions undertaken by, the Government of Panama, OFAC understands that the Government of Panama is working to sever the SDNTs’ ownership and control of the Felix Maduro Group, in an effort to protect the Panamanian and U.S. financial systems from abuse.  The statement further clarifies the persons and transactions that would require authorization.

See the Burundi Sanctions Designations updates on OFAC’s website.

See the Kingpin Act Designations list updates on OFAC’s website.

See the Kingpin Act/Panama-related General License updates on OFAC’s website.

See the Statement on the Felix Maduro Group on OFAC’s website.

See OFAC’s recent actions page.

Need A Hand?

We would love to hear from you.  If there are subjects in this post that you would like to know more about, or if you need assistance with your compliance program, please contact us.

Sanctions This Week: March 28th-April 3rd, 2016


OSFI

On March 29th, 2016, the Office of the Superintendent of Financial Institutions (OSFI) released the United Nations Security Council’s (UNSC) ISIL (Da’esh) and Al-Qaida sanctions update to the sanctions list, adding a single individual.

The individual is subject to the assets freeze, travel ban and arms embargo set out in paragraph 2 of Security Council resolution 2253 (2015) adopted under Chapter VII of the Charter of the United Nations.  The individual added is Saudi Arabian and holds a Qatari passport.  He is currently residing in Afghanistan and has led an Al-Qaida battalion in Afghanistan since at least mid-2010.Rodney_Money_Clothesline4

See the update on the United Nations (UN) website.

Go to the OSFI lists page.


OFAC

The U.S. Department of Treasury’s Branch, The Office of Foreign Asset Control (OFAC), released two updates last week.  One was related to the removal of the Highly Enriched Uranium (HEU) Agreement Assets Control Regulations, and the second, was adding three individuals and two entities to the Counter Terrorism Designations Lists.  OFAC also released the 3rd Quarter FY2014 Report for licensing activities undertaken pursuant to the Trade Sanctions Reform and Export Enhancement Act of 2000 (TSRA).

OFAC administers and enforces economic and trade sanctions based on U.S. foreign policy and national security goals.  The sanctions target countries, regimes, terrorists, international narcotics traffickers, the proliferation of weapons of mass destruction, and other threats to the national security, foreign policy or economy of the U.S.  The additions mentioned above, related to the Counter Terrorism Designations update, were included due to the fact both the individuals and entities are linked to Al-Qaida and the Taliban.  They are all Pakistani nationals, with Saudi Arabian ID, and are reported to be currently residing in the UK.

See the Counter-Terrorism update on OFAC’s website.

See OFAC’s recent actions page.

Need A Hand?

We would love to hear from you.  If there are subjects in this post that you would like to know more about, or if you need assistance with your compliance program, please contact us.

Sanctions This Week: March 21-27, 2016

Rodney_Money_Clothesline4OSFI

There were no updates released from OSFI this week.

Go to the OSFI lists page.

OFAC

The U.S. Department of Treasury’s Branch, The Office of Foreign Asset Control (OFAC), released two updates last week, related to the Zimbabwe, Counter-Terrorism and Non-Proliferation Designation Lists.  A total of three individuals and six entities were added to the respective lists.  OFAC also released the publication of Iran-related General License I and related FAQs.

OFAC administers and enforces economic and trade sanctions based on U.S. foreign policy and national security goals.  The sanctions target countries, regimes, terrorists, international narcotics traffickers, the proliferation of weapons of mass destruction, and other threats to the national security, foreign policy or economy of the U.S.  All of the additions mentioned above were related to aviation, the names added were either connected to an avionics regime, or were the entity under which they were operating.  As for the Iran-related updates, in order to allow for more efficient processing of applications under the Statement of Licensing Policy for Activities Related to the Export or Re-export to Iran of Commercial Passenger Aircraft and Related Parts and Services, OFAC has issued General License I: Authorizing Certain Transactions Related to the Negotiation of, and Entry into, Contingent Contracts for Activities Eligible for Authorization Under the Statement of Licensing Policy for Activities Related to the Export or Re-export to Iran of Commercial Passenger Aircraft and Related Parts and Services.  OFAC also updated the Frequently Asked Questions Relating to the Lifting of Certain U.S. Sanctions under JCPOA.

See the Zimbabwe update on OFAC’s website.

See the Counter-Terrorism and Non-Proliferation update on OFAC’s website.

See OFAC’s recent actions page.

Need A Hand?

We would love to hear from you.  If there are subjects in this post that you would like to know more about, or if you need assistance with your compliance program, please contact us.


Is Your MSB Ready for a FINTRAC Exam?

Rodney_MSB2
We get a lot of questions about examinations conducted by the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC). While we’re happy to be able to help our customers in their examinations (you can check out our free resources for FINTRAC exams here), the responsibility during the examination will rest with the money services business (MSB), mainly with the MSB’s Compliance Officer.

FINTRAC’s expectations have changed dramatically, since MSB’s were first required to comply with the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) and its enacted regulations. In 2015, we noticed that there was a dramatic shift in focus of MSB examinations. FINTRAC’s examiners were much more interested in detailed procedures (documents that describe how MSBs are complying with the PCMLTFA and regulations), and the Risk Based Approach.

One of the most important things that MSBs can do to ensure that their AML compliance programs are up to date, and at the same time, prepare for FINTRAC examinations, is to read FINTRAC’s published guidance. Two important guidance topics published in 2015 are, the Risk-Based Approach Guide (this guide describes what is the risk-based approach) and the Risk-Based Approach Workbook for MSBs (this workbook is for MSBs looking to implement a risk-based approach). While guidance published by FINTRAC doesn’t carry the weight of law or regulation, it does provide valuable insight about FINTRAC’s expectations.

Another excellent source of information is FINTRAC’s published Policy Interpretations. These are FINTRAC’s official answers to questions asked by MSBs and other reporting entities.

In Person & Desk Examinations

Whether the FINTRAC exam is in person or desk (conducted by phone) examinations, they follow very similar formats. The key difference is the regulator’s ability to request additional operational data during onsite examinations.

It is ok for you to take notes throughout the examination process (and we recommend that you do). You are permitted to have a lawyer, consultant or other representative with you (if you do, FINTRAC will request that you complete the Authorized Representative Form in advance). While your representative cannot generally answer questions on your behalf, they can prompt you if you are nervous or stuck, and help you to understand what is being asked of you, if it is not clear.

If you do not speak English and/or French fluently, we highly recommend that you have a person present who can translate questions and responses for you.

If you are not certain what the examiner is asking for, you should always ask for clarification before answering.

For in person examinations, do not invite the examiner to have a pint, lunch or even a coffee. FINTRAC has very strict policies around bribery, to the extent that if I am out socially with an acquaintance who works for FINTRAC, I cannot pay for their tea. It may feel a little bit “over the top”, not to be able to extend these courtesies, but don’t be offended – it’s not you, it’s policy.

The Introduction

The examiner will provide a brief overview of the examination process as a formal opening to the examination. At the end of this introduction, the examiner will ask if you have any questions. At this point, it can be useful to provide a very brief (five minutes maximum) overview of your business.

Your introduction should reflect the materials that you have already submitted to FINTRAC (which ideally included an opening letter that described anything about the business that would not be readily apparent to the examiner, or anything that you believe could be misunderstood). Key facts about your business include:

  • Your corporate structure and ownership;
  • The types of products and services that are offered / types of transactions that are conducted;
  • Where your offices, agents and customers are located;
  • How you connect with and your customers; and
  • Anything significant that has changed since your last FINTRAC examination.

This synopsis must be very brief. If there is anything that is complex, it should be included as an explanation in your initial package (preferably in a simplified chart form – for example an ownership structure chart).

The examination will then begin. At the end of each section, the examiner will ask if you have any questions and let you know whether there are any deficiencies.

Part 1 – FINTRAC MSB Registration

In this part, FINTRAC will go through your MSB registration field by field and confirm that the information is accurate. The most common errors that we have seen are:

  • Not listing a trade name/operating name;
  • Not listing all relevant locations;
  • Listing bank accounts that are inactive or not listing bank accounts that are active;
  • Not including MSB or agent relationships (either buying from or selling to another MSB);
  • Incomplete ownership information; and
  • Senior Management and/or Compliance Officer information, that is out of date.

Although it is not technically part of the registration, some examiners will ask about the Compliance Officer’s responsibilities/duties at this stage.

Failure to update the MSB registration in the “prescribed form and manner” is the single most common deficiency for MSBs from 2008 to the present, accounting for deficiencies in 61% of examinations (according to FINTRAC data released in 2015).

Part 2 – Compliance Policies & Procedures

In this part, FINTRAC will ask questions about the policy and procedure documents that you have provided in advance of the examination. There are a few standard questions that are generally asked:

  • Who wrote the policies and procedures?
  • Were the versions submitted to FINTRAC the most recent versions?
  • When were they updated?
  • When and how do you identify your customers?
  • How do you ensure that identification is up to date?
  • How do you monitor transactions?
  • How do you recognize, document and monitor “business relationships” (note: this is any time that you have either an ongoing service agreement with a customer and/or your customer has performed two or more transactions that require identification).
  • What are indicators of a suspicious transaction?

The examiner will also ask a number of questions based on the documents that you have submitted, including questions about compliance-related processes.

Part 3 – Risk Assessment

In this part, FINTRAC will focus on your Risk Based Approach, asking specific questions about the Risk Assessment and related documents that you have provided in advance of your examination. Again, there are some common questions that are asked:

  • Do you have any high-risk customers or business relationships?
  • What factors do you consider in determining that a customer or business relationship is high risk?
  • How are customer due diligence and enhanced due diligence different (both generally, and in your processes and documentation)?

Most additional questions will be related to risk management processes. For example, it has been common in the last few months for examiners to ask if a customer or transaction could be rejected (“Yes, if it was outside of our risk tolerance.”)

This may also lead to questions about whether or not an Attempted Suspicious Transaction Report (ASTR) or Suspicious Transaction Report (STR) was filed. If there were reasonable grounds to suspect money laundering or terrorist financing, the answer should be yes, if not, you should explicitly say, “There were not reasonable grounds to believe that this event was related to money laundering or terrorist financing” then provide an explanation.

Part 4 – Operational Compliance & Reporting

In this part, the examiner will ask questions about specific transactions. Some of the cases that you must be ready to explain are:

  • A reportable transaction (generally an electronic funds transfer or EFT) was reported by another reporting entity;
  • A transaction matches an indicator of potentially suspicious activity (if there were reasonable grounds to suspect money laundering or terrorist financing, the answer should be yes, if not, you should explicitly say that “there were not reasonable grounds to believe that this event was related to money laundering or terrorist financing” then provide an explanation); and
  • Business relationships and ongoing monitoring (in particular, if this did not occur earlier in the examination).

During a desk examination, the examiners do not request additional materials.

During onsite examinations, it has become commonplace for examiners to request additional materials. These are generally related to:

  • Business relationships;
  • Ongoing monitoring (including the monitoring of business relationships),
  • High risk customers;
  • Enhanced due diligence; and
  • Other risk-based processes.

Be clear with the examiner about what can be extracted easily from your IT systems, and in the case that data cannot be extracted easily, be prepared to show the examiner an example (or several). If your system has an “auditor access” feature (generally read only access with search capability), it can be useful to set this up in advance of the onsite visit.

Exit Interview

Congratulations – you’ve made it to the finish line!

At this point, the examiner will sum up the findings (if there are any), and read a standard disclosure statement. For most of us, the disclosure statement is terrifying, as it talks about penalties. This is standard process – do not be alarmed. When the examiner has finished, you may ask if a penalty is being recommended (if you’re a worrier, please do this). Not all FINTRAC examiners will provide guidance at this stage, but it doesn’t hurt to ask.

The examiner will let you know when to expect a formal letter (generally within 30 days of the end of an examination).

After the Examination

You will receive a formal letter that details FINTRAC’s findings, as well as whether or not an Administrative Monetary penalty (AMP) is being recommended. In the case that there is a potential penalty, we recommend taking action as soon as possible). In most cases, FINTRAC does not require MSBs to submit an action plan (but your bank might still require that you do this, and it’s a good idea to keep a record of the actions that you’ve taken to correct any deficiencies).

Need a Hand?

If you are an MSB that needs compliance assistance preparing for an FINTRAC exam, remediating findings, or setting up an AML compliance program, please contact us.

FINTRAC Examination Results for MSBs

The Canadian Money Services Business Association (CMSBA) recently held their Spring Training events in Montreal, Vancouver and Toronto.  The list of speakers included MSB industry professionals, as well as representatives from regulators including the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC).  For a full synopsis of the Montreal and Toronto events, click here.  FINTRAC presented excellent statistical data about how MSBs have fared in examinations conducted between April 2011 and July 2014.  So how are MSBs faring?  Very well overall. 

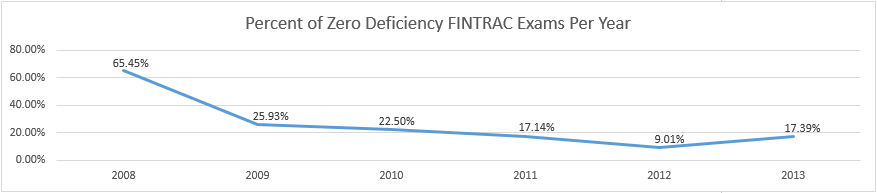
ZDE FINTRAC 2008-2013

Data obtained through a freedom of information request indicates that almost 25% of MSBs examined between 2008 and 2013 have not had any deficiencies.

How Does FINTRAC Decide Who Is Examined?

FINTRAC considers several factors when deciding which reporting entities (REs) will be examined.

  • Concurrent Examinations: examinations conducted in tandem with the Office of the Superintendent of Financial Institutions (OSFI). This is applicable to federally regulated financial entities (FRFEs) like banks.
  • Market Share: The largest reporting entities in Canada (because the larger an organization is, the more critical the risk of non-compliance will be);
  • Cyclical: Coverage of a whole industry (this seemed to apply most to Casinos).
  • Follow-Up: Subsequent examinations based, with an emphasis on the resolution of deficiencies found in previous examination(s) to ensure remediation. FINTRAC noted that although it is no longer a requirement to submit a formal action plan to FINTRAC, it is a best practice for REs to document (and update) an action plan internally.
  • Risk: FINTRAC’s evaluation of the RE’s risk, based on a broad selection criteria, such as money laundering and terrorist financing vulnerabilities, the likelihood of non-compliance and industry trends.
  • Theme-Based: Related to specific intelligence about a RE or type of business that indicates there may be an elevated risk of non-compliance, money laundering vulnerability or terrorist financing vulnerability.

Methodology & Analysis

FINTRAC’s statistical analysis of MSB adherence to the requirements laid out in the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) and its regulations is broken down by percentage, the results of the exams conducted that were fully compliant, partially compliant and non-compliant.  These are colour coded:

  • Green: fully compliant (no deficiencies were observed),
  • Yellow: partially compliant (there was something in place, but the MSB missed something), and
  • Red: non-compliant (in most cases, there was nothing in place or a reporting timeframe was missed).

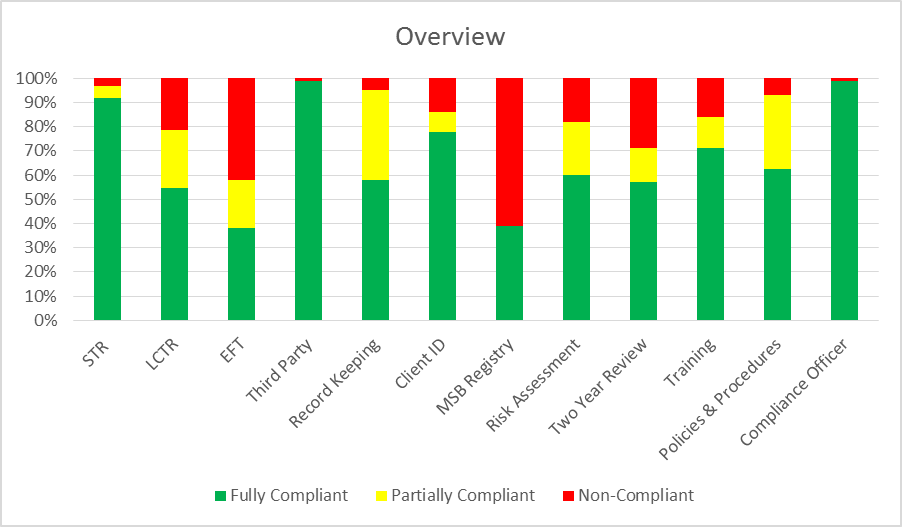
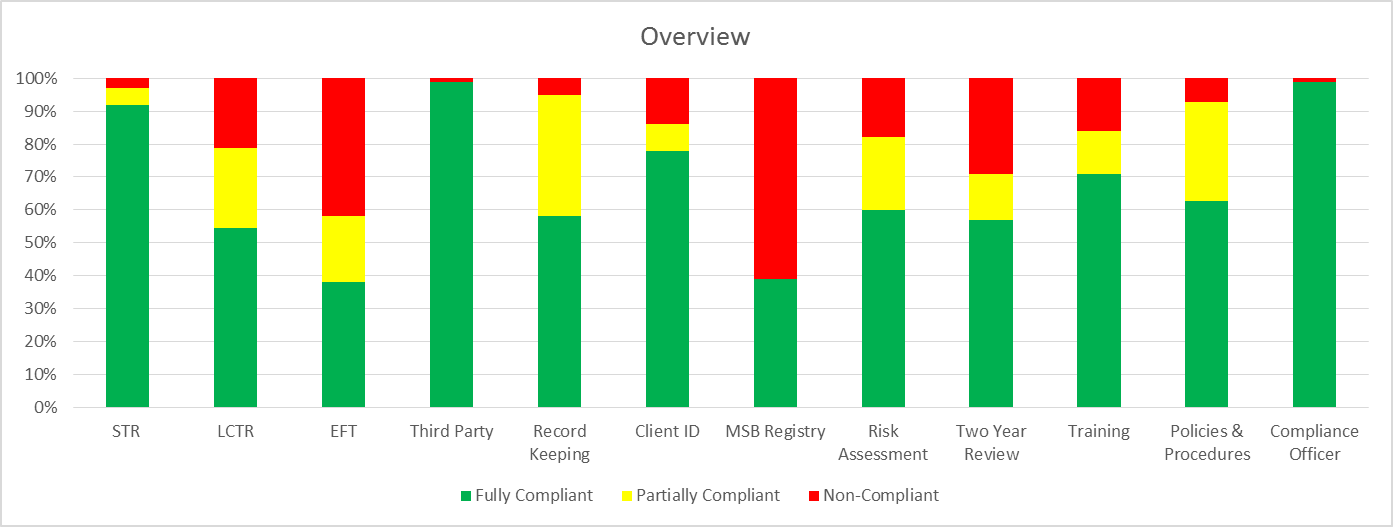
Overall examination results have been positive.

Overview

It’s noteworthy that if FINTRAC has, as of 2014, found something during an examination that is considered ‘immaterial’, it’s not cited.  For example, in a large sample, if there are two client addresses that appear to be PO boxes, but all other client addresses were complete and in acceptable formats, there may not be a citation.  In these cases, FINTRAC may inform the RE verbally, but it will not be part of the formal ‘findings’ letter.

Compliance Officer

MSBs are required to have a Compliance Officer (a person that is responsible for overseeing the AML & ATF compliance program).  The appointment of the Compliance Officer must be documented in writing.  FINTRAC staff chided that this is likely the easiest area to achieve a fully compliant result in examinations.  MSB examination results certainly reflected this.

CO Chart

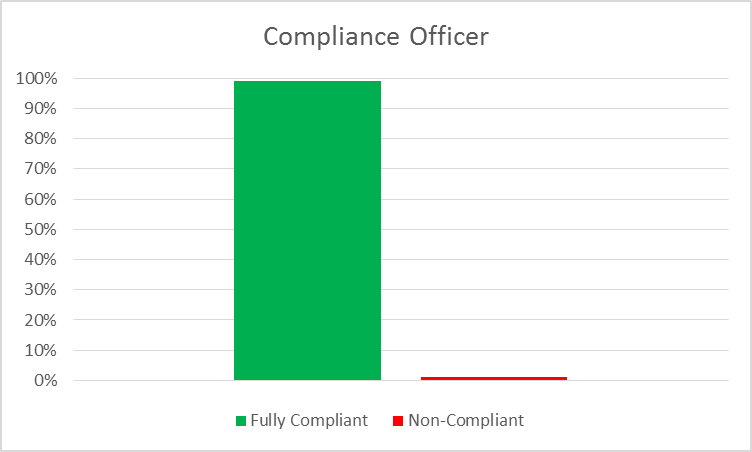
From a total of 612 MSB examinations considered, 608 MSBs were fully compliant.

Only four MSBs were deemed to be non-compliant.  It was noted that these were generally new market entrants that did not appear to understand Canadian AML & ATF compliance requirements.

Policies and Procedures

MSBs are required to have policies and procedures.  Policies describe the MSB’s regulatory obligations, while procedures describe what the MSB is doing to meet those requirements.  These must be documented, in writing, and the procedures must cover both staff and agents (if the MSB has agents).

PP Chart

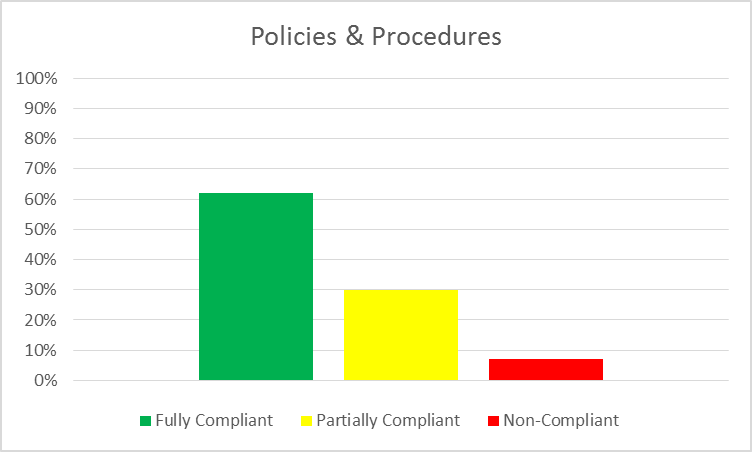
From a total of 765 MSB examinations considered, 477 MSBs were fully compliant.

In 230 examinations, MSBs were deemed to be partially compliant.  Common errors included:

  • The omission of the 24-hour rule (specific descriptions of how the MSB determined whether or not reportable transactions had occurred over a 24 hour period),
  • Third party determinations (specific descriptions of when an MSB must determine if there is a third party involved, as well as what information needs to be collected and recorded), and
  • Politically exposed foreign person (PEFP) determinations (specific descriptions of when an MSB must determine if their client is a PEFP, and if so, what information needs to be collected/recorded. There is also a requirement that senior management signoff on the account within 30 days of the determination).

A total of 55 MSBs did not have any documented policies or procedures. In some cases, FINTRAC noted that there appeared to be processes in place, but that these were not documented in writing.

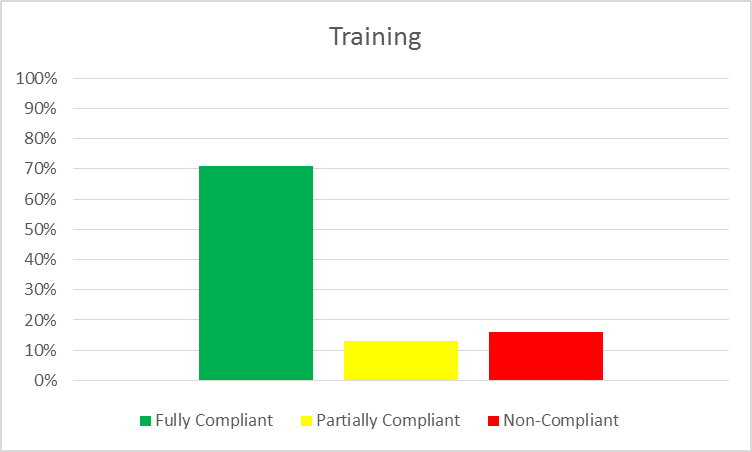
Training

MSBs are required to have an ongoing training program. The training program must be documented (who, what, where, when and how) and delivered to all staff and agents on an annual basis, at minimum.

Training Chart

From a total of 487 MSB examinations considered, 346 were fully compliant.

In 63 examinations, MSBs were deemed to be partially compliant.  Common errors included:

  • Interviews conducted with staff during an examination that evidenced a misunderstanding of the requirements (during an exam, FINTRAC will interview random staff members related to regulatory requirements to ensure training effectiveness)

In 78 examinations, MSBs did not have any training in place, or if they did, it was not documented.

Among the training options available to MSBs, we’re most excited about a relatively new offering from TAMLO that includes fast paced and visually stunning video content, as well as testing and tracking tools for Compliance Officers.

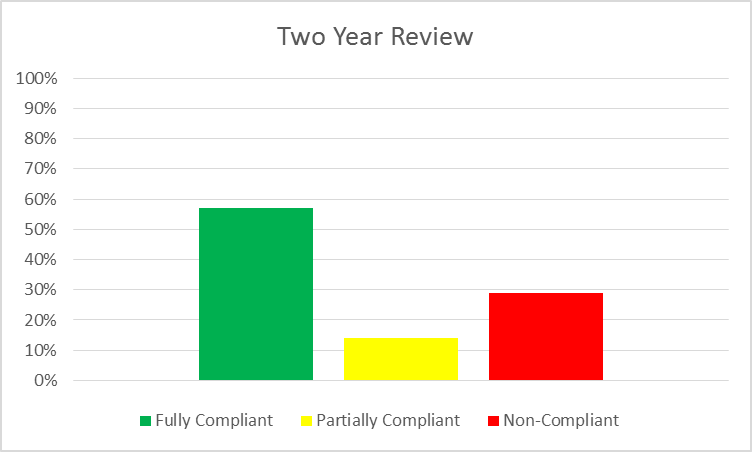
AML Compliance Effectiveness Review

MSBs are required to complete an AML Compliance Effectiveness Review once every two years.  The review must cover all policy and procedure documentation, as well as operational testing to ensure procedures are being properly followed.

2YR Chart

From a total of 722 MSB examinations considered, 412 were fully compliant.

In 101 examinations, MSBs were deemed to be partially compliant.  Where MSBs missed the mark was typically because they did not respect the two year cycle.  Other common errors included:

  • Only reviewing the policy documents with no operational testing of whether they are being followed (the policy document tells staff and agents what to do. Procedures tell them how to do it.  MSBs must be sure they are testing whether staff and agents are adhering to the procedures).

In 209 examinations, MSBs had not conducted an effectiveness review or could not provide evidence of one taking place.

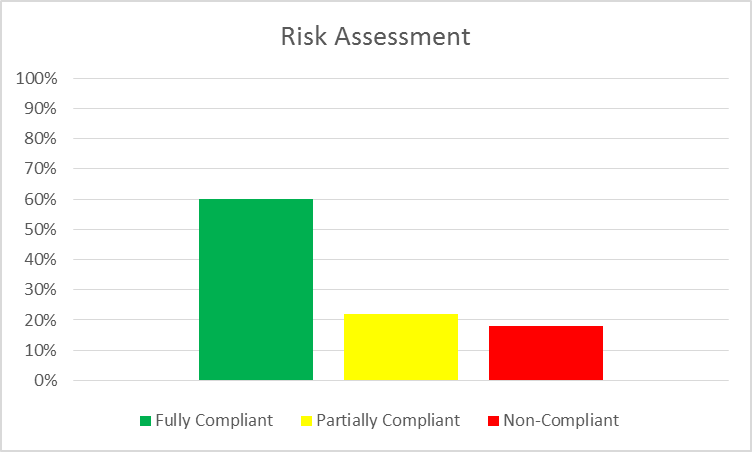
Risk Assessment

MSBs are required to assess the risk that their business could be used for money laundering or terrorist financing.  The risk assessment must include four key components:

  • Products, services and delivery channels;
  • Geography;
  • Customers; and
  • Any other relevant factors.

Risk must be assessed and scored, and mitigated by appropriate controls.

RA Chart

From a total of 720 MSB examinations considered, 432 were fully compliant.

In 158 examinations, MSBs were deemed to be partially compliant.  The main issue was failing to include one of the four required elements. In some cases, a risk assessment was in place, but the documentation was not sufficient in assessing the MSB’s risk and controls.

In 129 examinations, MSBs had no evidence of a risk assessment.

FINTRAC noted that additional industry-specific risk assessment guidance is expected to be published later this year.

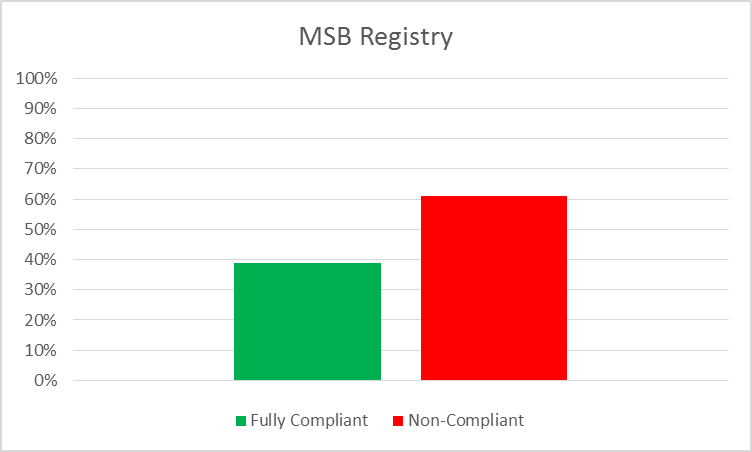
MSB Registration

MSBs are required to register with FINTRAC, as well as update their information within 30 days if there are any changes to business activities, banking or agent information.

MSB Reg Chart

From a total of 591 MSB examinations considered, 230 were fully compliant.

In this category, no partially compliant ratings were provided (the MSB registration was either complete, accurate and up to date, or it was deemed to be non-compliant).

In 361 examinations, MSBs were deemed to be non-compliant.  Most issues were due to a failure to update information when something within the business had changed or a failure to list all business activities. For example, the MSB registration may indicate that an MSB only performed foreign exchange in a case where remittance services were also provided.

Client Identification

MSBs are required to identify their clients in certain situations.  There are prescribed methods for completing this both in person and non-face-to-face (NF2F), and the identification document (ID) information must be recorded.

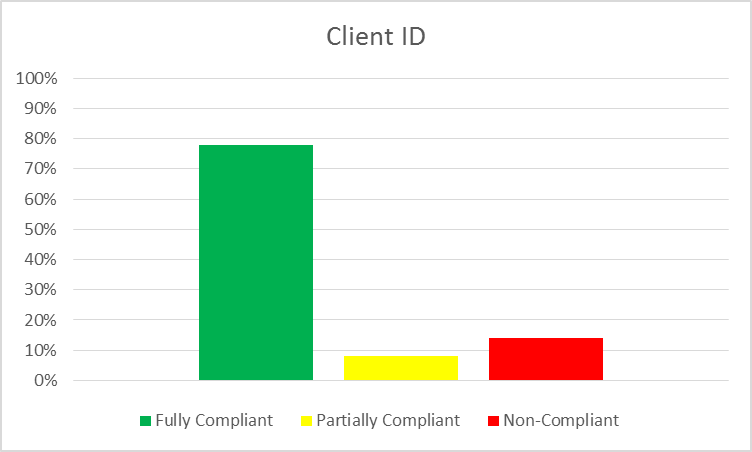
Client ID Chart

From a total of 796 MSB examinations considered, 621 were fully compliant.

In 64 examinations, MSBs were deemed to be partially compliant.  Common errors included:

  • Unacceptable ID (such as health card in Ontario);
  • Accepting ID that was expired at the time of the transaction (identification documents must be valid, or not expired, at the time they are reviewed);
  • Failing to record the prescribed details of the ID used (when reviewing a client’s ID, MSBs must keep a record of certain prescribed information); and
  • In Non-Face-To-Face Identification situations, only using one method, or using an unacceptable combination of methods (when identifying a customer who is not physically present, there are prescribed methods of how this is to be accomplished).

In 111 examinations, MSBs were non-compliant with client identification requirements.

Record Keeping

MSBs are required to keep certain records related to transactions and client identification.  These records must be stored in a manner that they can be accessed in the event they are requested, and must be maintained for at least five years.

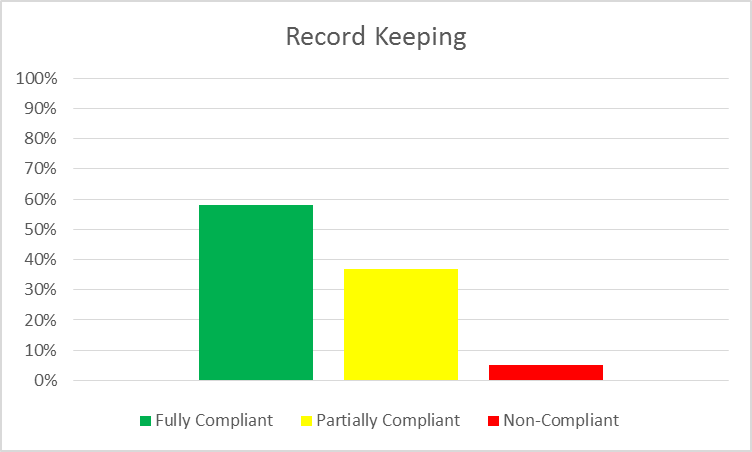
RK Chart

From a total of 811 MSB examinations considered, 470 were fully compliant.

In 300 examinations MSBs were deemed to be partially compliant.  In these cases, record keeping was taking place but elements of the record keeping requirements were being overlooked.  Common issues included:

  • Missing telephone numbers;
  • Vague occupation information (for example “manager” or “worker”);
  • PO boxes recorded as customer addresses;
  • Missing postal codes;
  • Third party determinations that were incomplete; and
  • Payment methods for incoming and outgoing payments.

In 41 examinations, MSBs were non-compliant with record keeping requirements.

Third Party Determinations

MSBs are required to make a third party determination in certain prescribed circumstances, as well as collect and record certain information (name, address, date of birth, occupation and relationship to your client) about the third party.

TPD Chart

The total number of MSBs included in the review was not provided, with the statement: “there was not enough information available to conduct reasonable analysis”.  However, the total number of non-compliant MSBs was 6, indicating that approximately 600 MSB examinations were considered in this sample.

FINTRAC Reporting

When FINTRAC assesses reporting obligations, it uses the internal acronym “QTV”, which stands for quality, timing and volume.  Quality refers to the information in the report, specifically, if the report has all the required information.  Timing simply means, was the report filed within the designated timeframe.  Volume is slightly more complicated, but mainly refers to the amount of reports you have filed compared to your previous submissions.  It was noted that typically, where MSBs were deemed partially compliant, it was due to the quality.  Where non-compliance was related to the timing.

Electronic Fund Transfers Reports

MSBs are required to submit electronic funds transfer (EFT) reports to FINTRAC within 5 business days from the date the transaction took place.  An EFT includes the international transfer of CAD 10,000 or more, either in a single transaction, or multiple transactions within a 24-hour period.

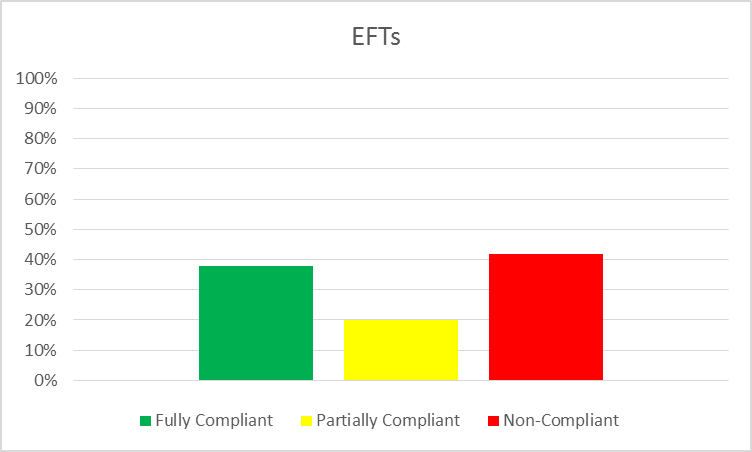
EFT Chart

From a total of 434 MSB examinations considered, 165 were fully compliant.

In 87 examinations, MSBs were deemed to be partially compliant. MSBs were typically failing to include all required information, such as:

  • Phone number;
  • Date of birth; or
  • Postal code.

It is noteworthy that while not all fields are marked as required in F2R, all fields must be filled in if the MSB has recorded the information.

In 182 examinations, MSBs were deemed non-compliant, with most not reporting the EFTs within the specified time frame, and a small portion missing EFT reports.

Large Cash Transaction Reports

MSBs are required to submit large cash transaction (LCT) reports to FINTRAC within 15 calendar days from the date of the transaction, if the transaction was CAD 10,000 or more in cash, either in a single transaction, or multiple transactions within a 24-hour period.

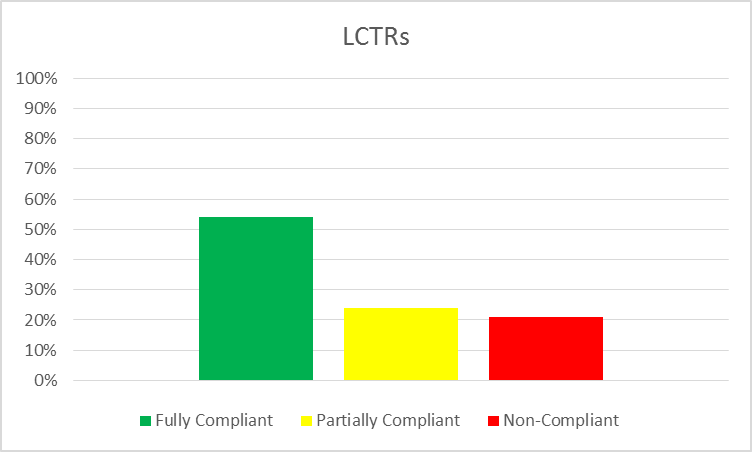
LCTR Chart

From a total of 428 MSB examinations considered, 232 were fully compliant.

In 104 examinations, MSBs were deemed to be partially compliant.  MSBs were typically failing to include all required information, such as:

  • Occupation;
  • Date of birth;
  • Postal code; or
  • Type of ID used to identify the client.

In 92 examinations, MSBs were non-compliant, with most not reporting the LCTs within the specified time frame, and a small portion missing LCT reports.

Suspicious Transaction Reports

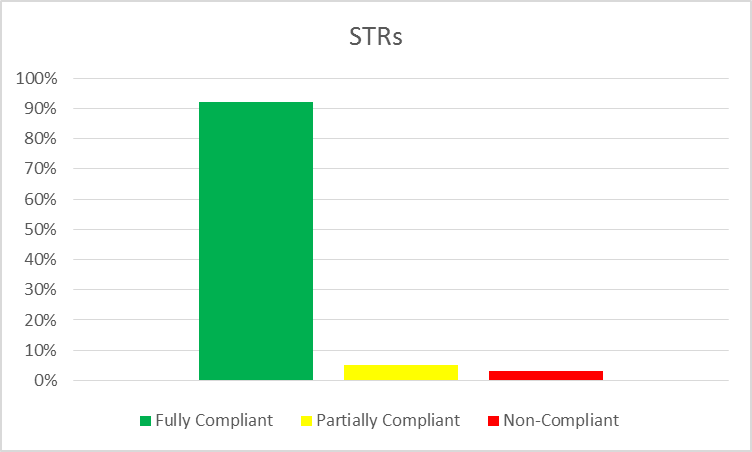
MSBs are required to submit suspicious transaction reports (STRs) and attempted suspicious transaction reports (ASTRs) to FINTRAC within 30 calendar days from the date the transaction is deemed suspicious by the Compliance Officer.

STR Chart

From a total of 285 MSB examinations considered, 262 were fully compliant.

In 14 examinations, MSBs were deemed to be partially compliant.  In these cases, MSBs were typically failing to include all required information.

In 9 examinations, MSBs were non-compliant.  Failing to file STRs carries relatively sever penalties, as the Canadian intelligence community relies on this type of reporting to build cases.  Where items are escalated as being potentially suspicious (either by staff or a transaction monitoring system), MSBs should always document the reason that these items are deemed not to be suspicious if no STR or ASTR reporting is completed.

Need a Hand?

If you are an MSB that needs compliance assistance (or a bank that wants assistance in setting up and maintaining a compliance regime that effectively manages MSB related risk), please contact us.


Insights From the CMSBA Education Days

We were fortunate enough to be able to attend the Canadian MSB Association (CMSBA)’s Montreal and Toronto spring training days. For Money Services Businesses (and those affiliated with the industry), the CMSBA is an excellent resource for collaboration, information sharing and advocacy. For those that were not able to attend any of the spring training sessions, here’s a roundup of the topics covered.

FINTRAC & MSB Compliance Examinations

Canada’s federal regulator for anti-money laundering (AML), the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC), provided in depth statistics related to compliance examinations, as well as common issues for MSBs. Despite what some highly publicized administrative monetary penalties (AMPs) may lead you to believe, MSBs are faring well as a sector in FINTRAC’s compliance examinations. It’s noteworthy that through a freedom of information request, Outlier obtained data on the number of MSBs that did not have any deficiencies in examinations. Between 2008 and the end of 2014, this amounted to approximately 25% of all MSBs examined. In most cases, MSBs were largely compliant, with some partial deficiencies.

Overview Big

For a complete breakdown of common issues noted in examinations, click here.

AMF, Respondents & Digital Currency

Québec’s provincial regulator, the Autorité des Marchés Financiers (AMF), provided clarification on its expectations for MSB respondents. For MSBs dealing with customers in Québec that do not have offices in the province, a respondent must be nominated to deal with the AMF on the MSB’s behalf. Among the requirements are that the respondent must:

  • Be over 18 years old;
  • Have an address in Québec (home address or business address); and
  • Not be under tutorship, curatorship or advisorship.

The AMF also addressed digital currency, noting that not all digital currency business models are covered by the Québec MSB Act, and that there must be an element of fiat currency involved in the transactions. Both the AMF’s press release from February 2015 and the current presentation confirmed that digital currency trading platforms (that include fiat currency transactions) and digital currency ATMs are considered in scope. As there are a myriad of other digital currency related business models, if you are unsure of where you fit, you can contact the AMF and receive a decision (we recommend that you request a decision in writing where possible).

Agency Agreements

I had the honour of speaking about MSB agency agreements (the agreements between MSBs and their agents) with Susan Han (previously of AUM Law). Like most things, agent agreements should be documented in writing and clearly spell out the terms of the agreement. MSBs that take on agents should understand that the MSB would bear most of the risk (financial, compliance and reputational). Agents should be aware that the client (and information about the client) “belongs” to the MSB rather than the agent (and this information should always be provided to the MSB when it is requested).

International Collaboration & De-Risking

The CMSBA has partnered with MSB associations worldwide to increase awareness of the negative ways in which de-risking (which CMSBA Director Ken Saul noted should be called de-banking) affects the financial system. As the de-risking issue has affected MSBs worldwide, and there does not appear to be any effective solutions under consideration, a whitepaper was developed and presented to the Financial Action Task Force (FATF). This whitepaper has received a positive reception. Stay tuned for more on the international efforts in this regard.

One of the few Canadian Financial Institutions that (openly) banks MSBs, Luminus Financial, was on hand to discuss factors that MSBs should consider when dealing with banking relationships. MSBs should be prepared to provide complete and transparent information about their business. In order to achieve success in both obtaining and maintaining banking relationships, MSBs should be able to demonstrate that they are compliant and present information in a way that is well organized and addresses all of the questions and requests that the bank has made. In some cases, this will be a higher standard than simply meeting the minimum compliance requirements set out in law and regulation.

Compliance Maturity Model

In looking proactively at issues related to de-risking and demonstrating compliance, the CMSBA is working to develop a compliance maturity model (CMM). Currently, CMSBA members can complete the first stage of this model by completing an attestation form online. The attestation states that the MSB is compliant with applicable legislation and not subject to administrative or criminal proceedings. Questions, comments or suggestions related to the CMM can be directed to cmsba-cmm@canadianmsb.org.

Need a Hand?

If you are an MSB that needs compliance assistance (or a bank that wants assistance in setting up and maintaining a compliance regime that effectively manages MSB related risk), please contact us.


Who Wins The De-Risking Shell Game?

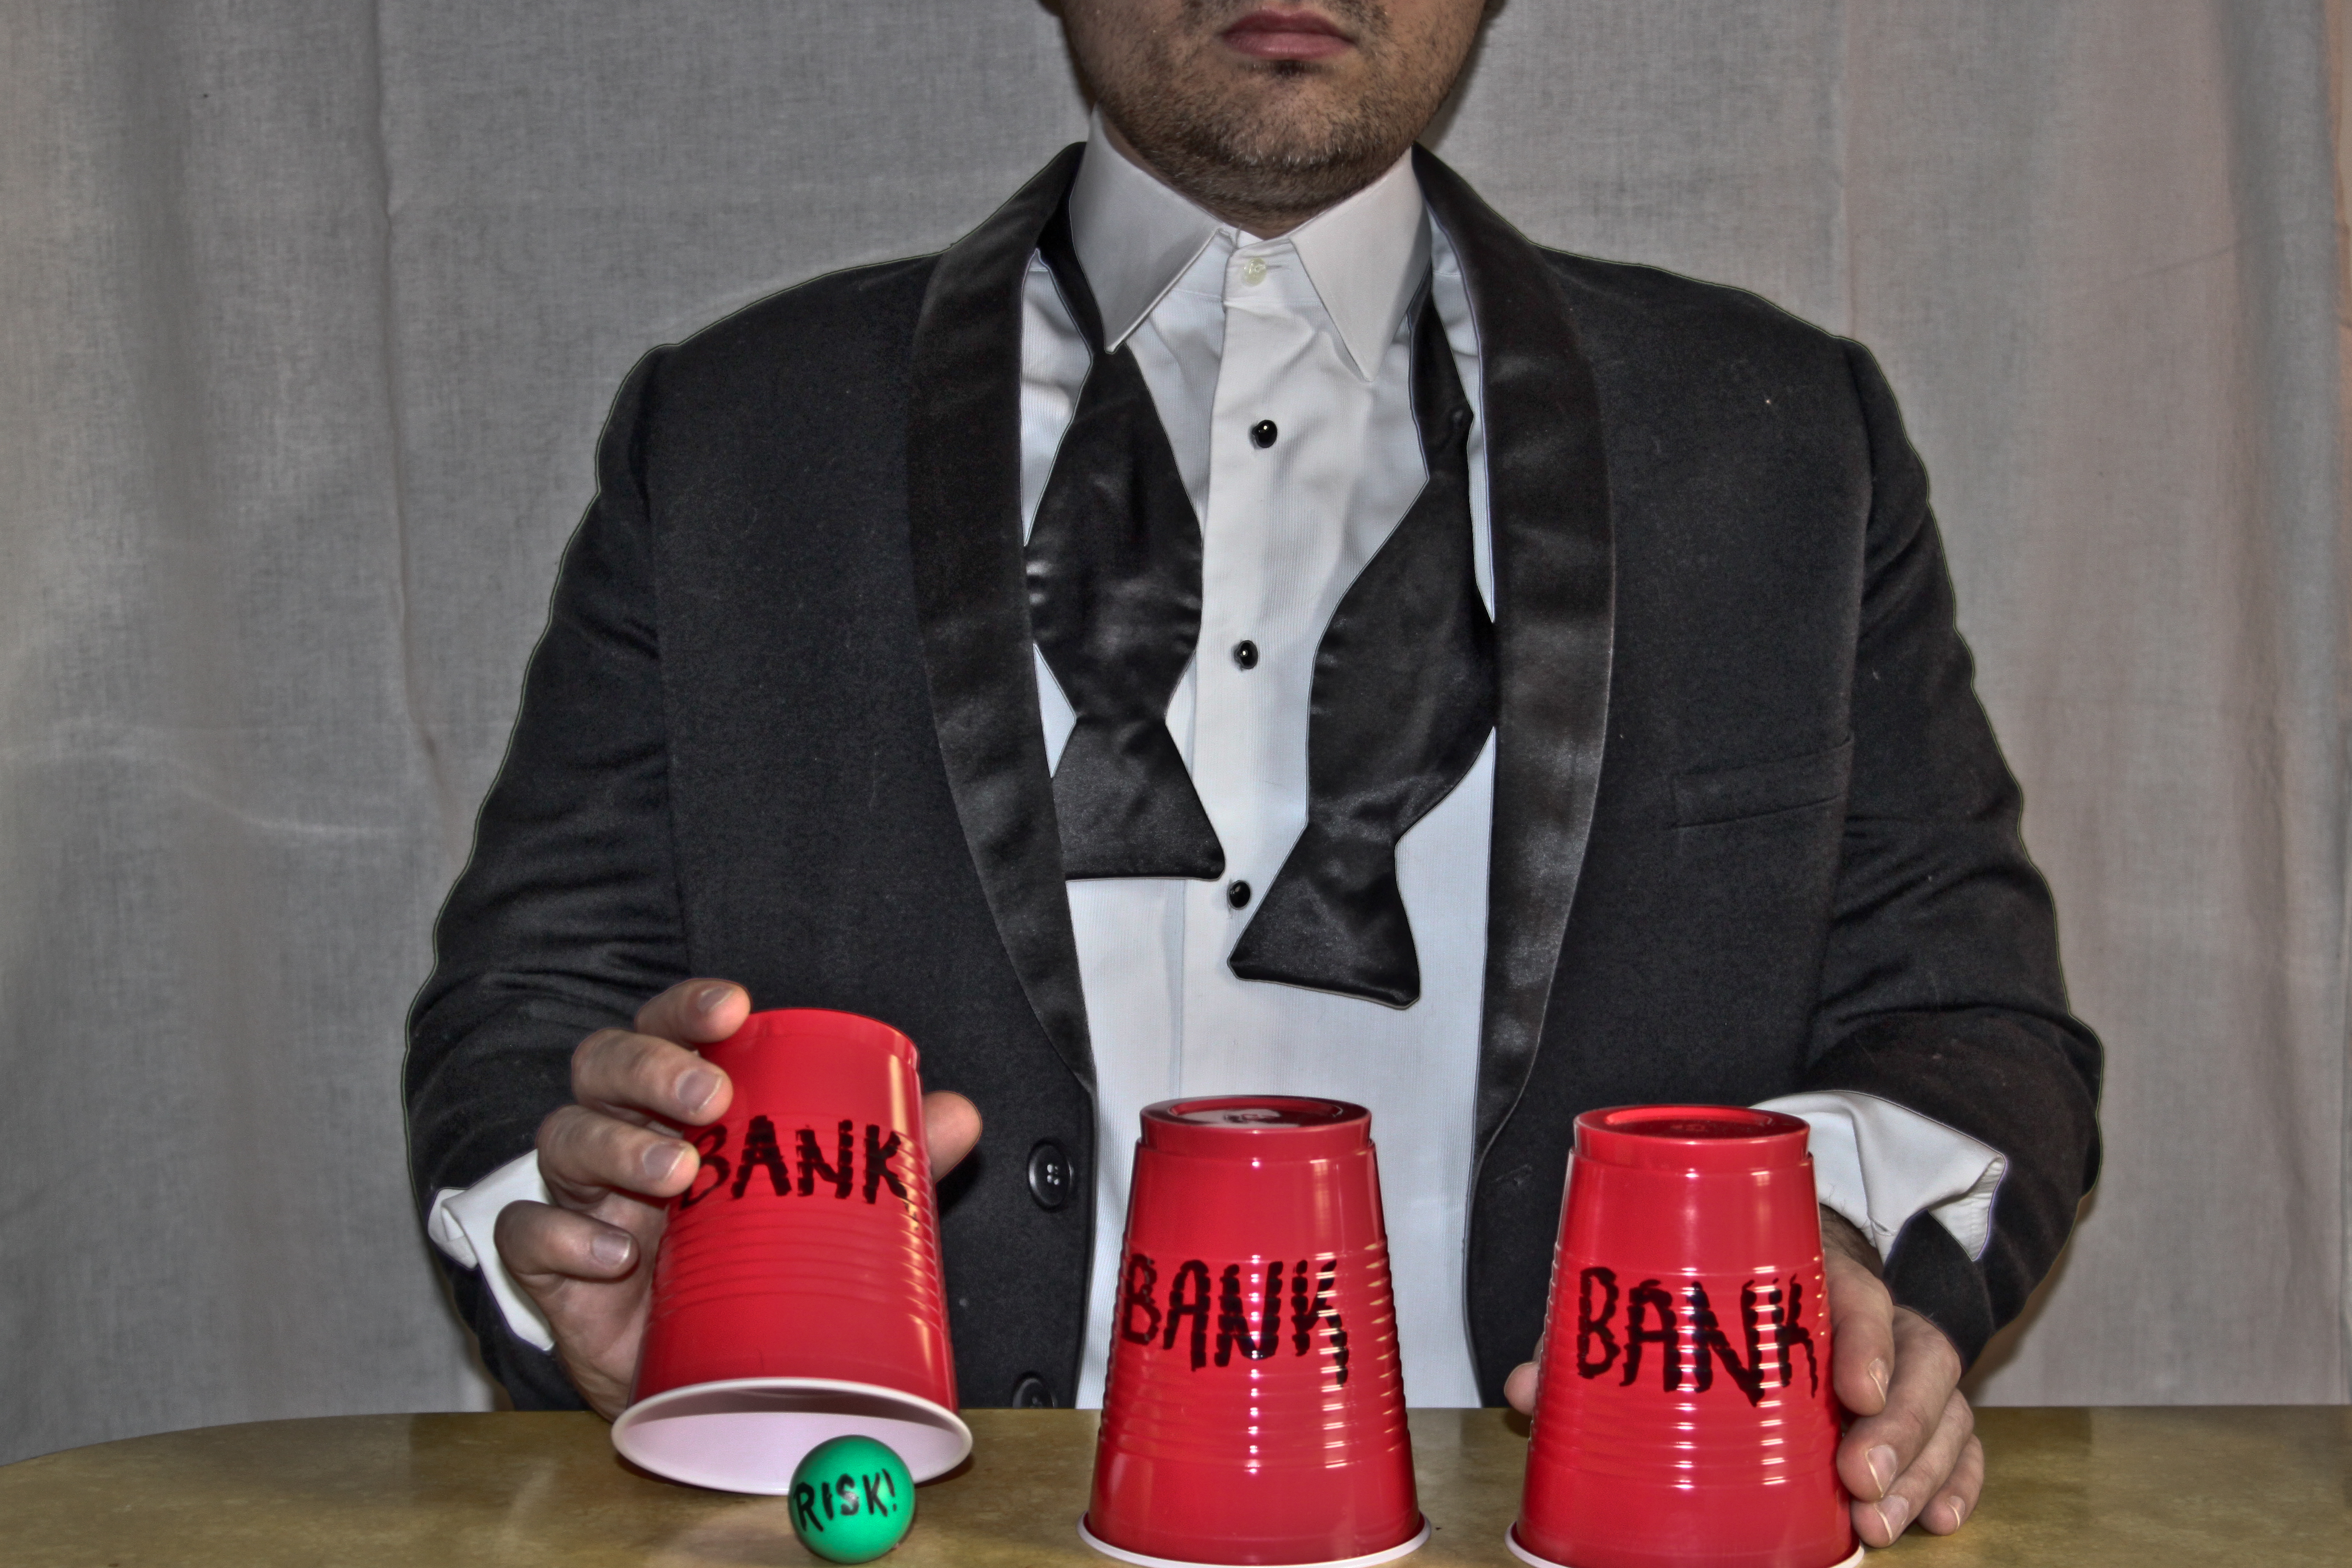
BankRisk_2The volume of evidence, both empirical and anecdotal, grows every day. The story on the surface is simple enough: banks are making the decision to “de-risk” (a polite way to say close the account of) certain types of businesses including money service businesses (MSBs) and digital currency businesses that are considered “too risky” by traditional financial services providers. The unintended consequences have included strained remittance corridors and frustration for businesses struggling to get by without reliable banking services. While these consequences are well documented, there are other unintended consequences of the de-risking phenomenon that have been less widely discussed. These include a growing lack of transparency between some industries and their banking service providers and directly threatens our ability to effectively manage money laundering and terrorist financing risk at both the financial institution and national levels.

It’s a shell game of “hide the risk” – and we’re all losing.

Businesses Are Losing

By now, if you haven’t heard about businesses struggling to survive without access to banking facilities, you would have had to ignore financial media for the past two years. The global effects of de-risking have attracted the attention of the G-20, the Financial Action Task Force (FATF), Financial Crimes Enforcement Network (FinCEN), the World Bank, and many more. While it’s clear that there are issues in terms of access to banking, let’s be honest with one another: while some businesses will close up shop, many others will take a different track.

Whether it’s using alternative financial service providers, payment processors, personal bank accounts or merely opening accounts at other financial institutions without revealing the true nature of the underlying activity, businesses will find a way to carry on. I’ve spoken personally to businesses that have taken these approaches, and it has never been their first or most ideal choice. These aren’t criminals carrying on some nefarious business! They are entrepreneurs who would rather be able to provide their real business plan to their banks and explain their activity honestly, but they do not believe that this option is open to them.

Banks Are Losing

Consequently, a bank with a policy that prohibits these types of businesses from holding accounts will deal with businesses that have gone to great lengths to conceal the true nature of their activity. The banks are unaware of the true nature of the activity passing through their accounts, and therefore ill equipped to manage the risk related to these activities. The strain on banking resources must be phenomenal, as banks must constantly devise new ways to interpret patterns of customer activity to detect undeclared MSB or digital currency activity. While it isn’t easy to quantify these costs, I can only surmise that the cost of this detective work must be high, despite being ineffective.

To further muddy the waters, businesses who fail to provide transparent information to their banks for fear of de-risking may also conduct completely legal activities in a way that starts to look like criminal activity. For example, if you believe that your business banking relationship is not reliable, you may open many accounts (in some combination of personal and business names) and conduct fractions of your banking through each, transferring funds from one account to another as needed to meet your obligations. On the surface, it can seem much like “layering” or “structuring” activity (techniques used by money launderers to make funds more difficult to trace). This further adds to the banks’ burden by creating more activity that must be monitored and investigated.

Entire Nations Are Losing

It has been widely publicized that in some cases like Somalia, entire nations that are dependent on remittance payments from friends and family living and working abroad are experiencing increased difficulty. Reliable and cost-effective remittance payment providers are a shrinking pool. This seems absurd in a time when technology can facilitate a payment in seconds.

National Security Is Losing

It’s not just far-flung places dependent on remittance payments that are losing. Here at home, we have a national security system that is dependent on our financial intelligence units (FIUs) having access to reliable data. The reliability of that data is undermined at every level by the de-risking shell game:

  • Businesses do not declare the true nature of their activity – and there are no incentives for them to do so;
  • Banks do not understand the nature of their customers’ activities, making it difficult detect potentially criminal activity; and
  • There is likely to be an increase in “false positives”, where activity conducted by businesses that do not believe that they can reveal the true nature of their activity to their banks instead conduct business in a manner that resembles criminal money laundering techniques.

Taken together, this results in the likelihood that key information is not being reported to FIUs correctly. Consequently, it becomes more difficult for law enforcement and other national securities to rely on this data to perform their roles effectively.

Who Is Winning?

There are two potential winners in this game and much like the shell games that you see duping tourists on the streets of large cities, neither is without malevolent intent.

The first are unregistered/unlicensed MSB businesses. These are businesses that have ignored regulatory requirements and carried on business without any FIU reporting. In some cases, these businesses will even minimize their interaction with the local financial system by using foreign bank accounts (and point of sale terminals) to collect customer funds. While the risk of penalty is high, the reward for these businesses (in particular where they are able to complete transactions that pose a challenge for their compliant counterparts) can also be high.

The second is criminal organizations. When legitimate businesses are performing transactions that look like money laundering, detecting true criminal activity becomes exponentially more difficult. I can only assume that the criminals are laughing all the way to the bank.

Shutting Down The Shell Game

De-risking is a complex problem with complex outcomes, but the solution need not be complicated. It does, however, involve the cooperation of all levels of the financial services community: regulators, banking service providers and businesses.

The costs and benefits of de-risking need to be reassessed. Where banking service providers are capable of accepting and managing accounts for businesses considered to be “higher risk”, they should do so, with their regulator’s blessing. Rather than perpetuating the shell game, regulators should encourage banking service providers to manage risk (and provide solid guidance with reference to how this should be done). Finally, there should be open communication between banking service providers, regulators and business banking customers. The lines of communication closed by de-risking must be opened, allowing banks to have honest conversations that will provide real insight into their customers’ business and lead to effective long-term risk management.

Return to Blog Listing