PROCESSING...

Anti-Money Laundering
Consulting Services & Strategies

0 Items - Total: $0.00 CAD

Sanctions This Week: April 25th – May 1st, 2016

OSFIOutlier3_032

There were no updates released from OSFI this week.

Go to the OSFI lists page.

OFAC

The U.S. Department of Treasury’s Branch, The Office of Foreign Asset Control (OFAC), released one update to the Belarus-related Executive Order (EO) 13405 sanction list last week.  The original list was replaced and superseded by the new version, which was effective October 30th, 2015.  The EO names nine (9) entities, who are undermining the democratic processes or institutions in Belarus, as well as any entity or individual who directly, or indirectly, owns or controls 50% or more of the listed entities.

OFAC administers and enforces economic and trade sanctions based on U.S. foreign policy and national security goals.  The sanctions target countries, regimes, terrorists, international narcotics traffickers, the proliferation of weapons of mass destruction, and other threats to the national security, foreign policy or economy of the U.S.  The changes to the Belarus-related EO require any U.S. person(s) engaging in transactions involving, directly or indirectly, any of the entities described above, no later than 30 days after the execution of any such transaction in excess of $50,000, or any series of such transactions exceeding $50,000, to file a report with the U.S. Department of State, Office of Eastern European Affairs.  Reports to be filed, must include:

  • The estimated or actual dollar value of the transaction(s), as determined by the value of the goods, services, or contract;
  • The parties involved;
  • The type and scope of activities conducted; and
  • The dates or duration of the activities.

See the Belarus-related Executive Order update on OFAC’s website.

See OFAC’s recent actions page.

Need A Hand?

We would love to hear from you.  If there are subjects in this post that you would like to know more about, or if you need assistance with your compliance program, please contact us.

Sanctions This Week: April 18th-24th, 2016

Outlier3_036

OSFI

On April 20th, 2016, the Office of the Superintendent of Financial Institutions (OSFI) released the United Nations Security Council’s (UNSC’s) Al-Qaida and Taliban regulations update to the sanctions list, adding five individuals.

The individuals are subject to the assets freeze, travel ban and arms embargo set out in paragraph 2 of Security Council resolution 2253 (2015) adopted under Chapter VII of the Charter of the United Nations.  He individuals listed hold the following titles:

  • Head of religious compliance police and a recruiter of foreign terrorist fighters for Islamic State in Iraq and the Levant (ISIL);
  • lead oil and gas division official of Islamic State in Iraq and the Levant (ISIL);
  • Leader of an Indonesia-based organization that has publicly sworn allegiance to Islamic State in Iraq and the Levant (ISIL);
  • Leader and armed groups in Gaza using money to build an ISIL presence in Gaza; and
  • Served as the acting emir of Jemmah Anshorut Tauhid (JAT) since 2014 and has supported Islamic State in Iraq and the Levant (ISIL).

All of these individuals are of different nationalities, but all have connections to ISIL and have been designated as such.

See the update on the United Nations (UN) website.

Go to the OSFI lists page.

OFAC

The U.S. Department of Treasury’s Branch, The Office of Foreign Asset Control (OFAC), released two updates last week.  One update was related to the addition of an individual to the Libya Sanctions list.  The second update was the publication of new Cuba-related Frequently Asked Questions (FAQ), related to the recent changes made to the sanctions that had previously been placed on Cuba.

OFAC administers and enforces economic and trade sanctions based on U.S. foreign policy and national security goals.  The sanctions target countries, regimes, terrorists, international narcotics traffickers, the proliferation of weapons of mass destruction, and other threats to the national security, foreign policy or economy of the U.S.  The changes to the Libya sanctions list included the addition of the Prime Minister and Defense Minister of the National Salvation Government, who has been added due to contributions to the situation in Libya.

See the Cuba-related FAQ update on OFAC’s website.

See the Libya sanction list update on OFAC’s website.

See OFAC’s recent actions page.

Need A Hand?

We would love to hear from you.  If there are subjects in this post that you would like to know more about, or if you need assistance with your compliance program, please contact us.

Is Your MSB Ready for a FINTRAC Exam?

Rodney_MSB2
We get a lot of questions about examinations conducted by the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC). While we’re happy to be able to help our customers in their examinations (you can check out our free resources for FINTRAC exams here), the responsibility during the examination will rest with the money services business (MSB), mainly with the MSB’s Compliance Officer.

FINTRAC’s expectations have changed dramatically, since MSB’s were first required to comply with the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) and its enacted regulations. In 2015, we noticed that there was a dramatic shift in focus of MSB examinations. FINTRAC’s examiners were much more interested in detailed procedures (documents that describe how MSBs are complying with the PCMLTFA and regulations), and the Risk Based Approach.

One of the most important things that MSBs can do to ensure that their AML compliance programs are up to date, and at the same time, prepare for FINTRAC examinations, is to read FINTRAC’s published guidance. Two important guidance topics published in 2015 are, the Risk-Based Approach Guide (this guide describes what is the risk-based approach) and the Risk-Based Approach Workbook for MSBs (this workbook is for MSBs looking to implement a risk-based approach). While guidance published by FINTRAC doesn’t carry the weight of law or regulation, it does provide valuable insight about FINTRAC’s expectations.

Another excellent source of information is FINTRAC’s published Policy Interpretations. These are FINTRAC’s official answers to questions asked by MSBs and other reporting entities.

In Person & Desk Examinations

Whether the FINTRAC exam is in person or desk (conducted by phone) examinations, they follow very similar formats. The key difference is the regulator’s ability to request additional operational data during onsite examinations.

It is ok for you to take notes throughout the examination process (and we recommend that you do). You are permitted to have a lawyer, consultant or other representative with you (if you do, FINTRAC will request that you complete the Authorized Representative Form in advance). While your representative cannot generally answer questions on your behalf, they can prompt you if you are nervous or stuck, and help you to understand what is being asked of you, if it is not clear.

If you do not speak English and/or French fluently, we highly recommend that you have a person present who can translate questions and responses for you.

If you are not certain what the examiner is asking for, you should always ask for clarification before answering.

For in person examinations, do not invite the examiner to have a pint, lunch or even a coffee. FINTRAC has very strict policies around bribery, to the extent that if I am out socially with an acquaintance who works for FINTRAC, I cannot pay for their tea. It may feel a little bit “over the top”, not to be able to extend these courtesies, but don’t be offended – it’s not you, it’s policy.

The Introduction

The examiner will provide a brief overview of the examination process as a formal opening to the examination. At the end of this introduction, the examiner will ask if you have any questions. At this point, it can be useful to provide a very brief (five minutes maximum) overview of your business.

Your introduction should reflect the materials that you have already submitted to FINTRAC (which ideally included an opening letter that described anything about the business that would not be readily apparent to the examiner, or anything that you believe could be misunderstood). Key facts about your business include:

  • Your corporate structure and ownership;
  • The types of products and services that are offered / types of transactions that are conducted;
  • Where your offices, agents and customers are located;
  • How you connect with and your customers; and
  • Anything significant that has changed since your last FINTRAC examination.

This synopsis must be very brief. If there is anything that is complex, it should be included as an explanation in your initial package (preferably in a simplified chart form – for example an ownership structure chart).

The examination will then begin. At the end of each section, the examiner will ask if you have any questions and let you know whether there are any deficiencies.

Part 1 – FINTRAC MSB Registration

In this part, FINTRAC will go through your MSB registration field by field and confirm that the information is accurate. The most common errors that we have seen are:

  • Not listing a trade name/operating name;
  • Not listing all relevant locations;
  • Listing bank accounts that are inactive or not listing bank accounts that are active;
  • Not including MSB or agent relationships (either buying from or selling to another MSB);
  • Incomplete ownership information; and
  • Senior Management and/or Compliance Officer information, that is out of date.

Although it is not technically part of the registration, some examiners will ask about the Compliance Officer’s responsibilities/duties at this stage.

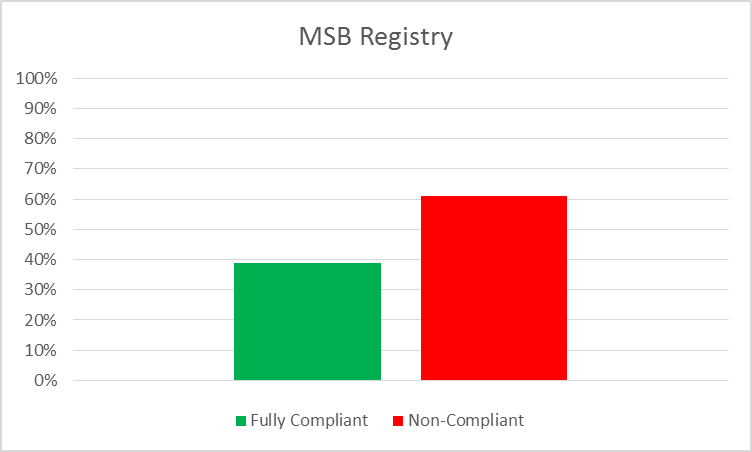
Failure to update the MSB registration in the “prescribed form and manner” is the single most common deficiency for MSBs from 2008 to the present, accounting for deficiencies in 61% of examinations (according to FINTRAC data released in 2015).

Part 2 – Compliance Policies & Procedures

In this part, FINTRAC will ask questions about the policy and procedure documents that you have provided in advance of the examination. There are a few standard questions that are generally asked:

  • Who wrote the policies and procedures?
  • Were the versions submitted to FINTRAC the most recent versions?
  • When were they updated?
  • When and how do you identify your customers?
  • How do you ensure that identification is up to date?
  • How do you monitor transactions?
  • How do you recognize, document and monitor “business relationships” (note: this is any time that you have either an ongoing service agreement with a customer and/or your customer has performed two or more transactions that require identification).
  • What are indicators of a suspicious transaction?

The examiner will also ask a number of questions based on the documents that you have submitted, including questions about compliance-related processes.

Part 3 – Risk Assessment

In this part, FINTRAC will focus on your Risk Based Approach, asking specific questions about the Risk Assessment and related documents that you have provided in advance of your examination. Again, there are some common questions that are asked:

  • Do you have any high-risk customers or business relationships?
  • What factors do you consider in determining that a customer or business relationship is high risk?
  • How are customer due diligence and enhanced due diligence different (both generally, and in your processes and documentation)?

Most additional questions will be related to risk management processes. For example, it has been common in the last few months for examiners to ask if a customer or transaction could be rejected (“Yes, if it was outside of our risk tolerance.”)

This may also lead to questions about whether or not an Attempted Suspicious Transaction Report (ASTR) or Suspicious Transaction Report (STR) was filed. If there were reasonable grounds to suspect money laundering or terrorist financing, the answer should be yes, if not, you should explicitly say, “There were not reasonable grounds to believe that this event was related to money laundering or terrorist financing” then provide an explanation.

Part 4 – Operational Compliance & Reporting

In this part, the examiner will ask questions about specific transactions. Some of the cases that you must be ready to explain are:

  • A reportable transaction (generally an electronic funds transfer or EFT) was reported by another reporting entity;
  • A transaction matches an indicator of potentially suspicious activity (if there were reasonable grounds to suspect money laundering or terrorist financing, the answer should be yes, if not, you should explicitly say that “there were not reasonable grounds to believe that this event was related to money laundering or terrorist financing” then provide an explanation); and
  • Business relationships and ongoing monitoring (in particular, if this did not occur earlier in the examination).

During a desk examination, the examiners do not request additional materials.

During onsite examinations, it has become commonplace for examiners to request additional materials. These are generally related to:

  • Business relationships;
  • Ongoing monitoring (including the monitoring of business relationships),
  • High risk customers;
  • Enhanced due diligence; and
  • Other risk-based processes.

Be clear with the examiner about what can be extracted easily from your IT systems, and in the case that data cannot be extracted easily, be prepared to show the examiner an example (or several). If your system has an “auditor access” feature (generally read only access with search capability), it can be useful to set this up in advance of the onsite visit.

Exit Interview

Congratulations – you’ve made it to the finish line!

At this point, the examiner will sum up the findings (if there are any), and read a standard disclosure statement. For most of us, the disclosure statement is terrifying, as it talks about penalties. This is standard process – do not be alarmed. When the examiner has finished, you may ask if a penalty is being recommended (if you’re a worrier, please do this). Not all FINTRAC examiners will provide guidance at this stage, but it doesn’t hurt to ask.

The examiner will let you know when to expect a formal letter (generally within 30 days of the end of an examination).

After the Examination

You will receive a formal letter that details FINTRAC’s findings, as well as whether or not an Administrative Monetary penalty (AMP) is being recommended. In the case that there is a potential penalty, we recommend taking action as soon as possible). In most cases, FINTRAC does not require MSBs to submit an action plan (but your bank might still require that you do this, and it’s a good idea to keep a record of the actions that you’ve taken to correct any deficiencies).

Need a Hand?

If you are an MSB that needs compliance assistance preparing for an FINTRAC exam, remediating findings, or setting up an AML compliance program, please contact us.

AML “Clearance Certificates” are a Scam

If you’ve received an email, letter or call telling you that a larger than usual sum of money is headed your way, but before it can be delivered to your bank, you are required to get a clearance certificate, you are being set up for a scam.

SCAM

The Setup

The scam goes by many names, but the setup is almost always the same…

Step 1: The Sexy Promise

The scammers need you to want to talk to them. To pique your interest, they’ll promise something that they think you will want. In most cases, it’s not a crazy sum of money that will be sent to you – most people would immediately recognize that as a scam. Instead, it will be a reasonable sum that is nonetheless attractive for your business.

In the most sickening cases that we’ve seen, the scammers have focused on charities by posing as potential donors. Outlier has even received a request for a clearance certificate from a “prospective client overseas.”

Step 2: The Legitimate Power

The scammers will claim that the certificate is being requested by a legitimate organization. Some of the scams that we’ve seen have said that certificates are required by:

  • Financial Transactions and Reports Analysis Centre of Canada (FINTRAC),
  • Financial Crimes Enforcement Network (FinCEN),
  • Office of the Currency Controller (OCC).
  • Securities Exchange Commission (SEC),
  • S. Department of Homeland Security,
  • International Monetary Fund (IMF), and
  • Financial Action Task Force (FATF).

None of these agencies issue, require, or have any other involvement with clearance certificates. In fact, if you call any of these agencies to ask about clearance certificates, they will tell you that you are likely the victim of a scam.

Step 3: The Real Threat

The type of “clearance certificate” that the scammers will ask for varies, but it’s usually something that most businesses have at least read about in the news, like “anti-money laundering” or “anti-terrorism.” It’s always something that sounds like it could be a real threat, although definitely not the type of threat that you would pose. Sometimes the requests will be phrased in a way that’s meant to make you feel a little bit indignant (“Why would this person think I’m a money launderer or a terrorist?!?)…

This is all part of the scam. If you’re emotional, you may not be thinking clearly, and it helps the scammer to build rapport with the victim. The scammer may offer consolations like, “Of course, I know that you’re not a criminal, but according to the * insert the authority from step 2 here * we must take these precautions…”

Step 4: Solving the Problem

The scammer is trying to collect as much information (especially financial information) as possible. The scammer will ask for your details directly (all for the purpose of obtaining the certificate, of course) or helpfully suggest a site for a “company” that can help you get your certificate.

Generally, this site requires a credit card payment (these may range from a few hundred to several thousand dollars). In more sophisticated scams, the site’s fine print states that the certificates are “not authorized by any government or international body” and that there are absolutely no refunds. This means that even if the victim reports the scam to their credit card company, they may not be able to issue a refund.

Step 5: Profit

At this stage, the scammers have the victim’s banking and/or credit card information. They may use this to conduct transactions (like draining the bank account or paying for things with the credit card), or simply sell the information on the dark web to other scammers.

Don’t Get Caught Up

It can be hard to believe that someone that you’ve been corresponding with, someone that seems like they could be good for business, is really just a scammer. It’s difficult, and embarrassing – but the sooner you exit the situation, the better off you are.

While you should report the incident (more about that below), it can be dangerous to attempt to bait the scammer to get more information about them (and the information that they provide is likely to be false in any case). Do collect as much information from your existing correspondence with the scammer (including screen captures and/or links to any websites that the scammer has provided you with), as these will be helpful in reporting the scam.

But if You Did, Protect Yourself

If you have already provided some, or all, of your financial details, it’s in your best interest to act quickly.   Contact your financial institution(s) and let them know what’s happened. They will be able to close your existing accounts, issue new accounts and review your recent transaction history with you.

Report It

At any point, you can report the scam to the Canadian Anti-Fraud Centre either online or by phone (1-888-495-8501).

Need A Hand?

While Outlier is not a law enforcement or investigative agency, we do conduct staff training sessions, including training related to common scams and how to recognize them. You can get in touch with us at info@outliercompliance.com or by using the online form.

Proposed AML Amendments & Credit Unions

Jon 1Today’s guest blogger is Jonathan Krumins, Vice-President, AML Risk & Compliance, at vCAMLO Solutions Inc. vCAMLO provides anti-money laundering (AML) and anti-terrorist financing (ATF) support to Canadian credit unions. You can learn more about vCAMLO at www.vcamlo.ca.

Background

On July 4, 2015, draft amendments to the Proceeds of Crime (Money Laundering) and Terrorist Financing Regulations (PCMLTFR) were published in the Canada Gazette. These changes are not yet in force, and are open to public comment until September 4, 2015. The proposed changes are based on requirements set out by the Financial Action Task Force (FATF), an inter-governmental body that sets out international standards for combating money laundering and terrorist financing. For this reason, we expect the final version of these amendments to be similar to the draft text.

2015 Proposed PCMLTFR Amendments and Credit Union Specific Analysis (Line By Line)

Why Do These Changes Matter to Credit Unions?

The proposed changes will have a direct impact on a Credit Union’s AML obligations, including record keeping, member identification and ongoing monitoring requirements. Some of the more significant changes include new member identification methods, expanded definitions (and requirements) for Politically Exposed Persons, and new record keeping requirements for “reasonable measures” taken.

New Member Identification Methods          

IdentificationThe draft regulations will require identification documents to contain a member’s name and photograph. This will exclude SIN cards and birth certificates as acceptable identification documents, and may pose an issue when identifying seniors whose passport or driver’s license has long since expired.

The amendments also provide a number of new identification methods that can be used to identify members both face-to-face and non-face to face. These new methods are an improvement on existing rules, which are currently more restrictive.

For example, a Canadian credit file meeting certain criteria could now be used to identify a member. Many credit unions perform credit checks as part of their account opening process, so this could be used in place of government-issued identification in certain circumstances, or would allow simple non-face to face identification.

Also added is the ability to rely on information from “a reliable source” (yet to be determined, but likely online databases and other web-based resources), and information confirming that an individual has a deposit account, credit card or other loan account with another credit union, bank or caisse populaire. A credit union will also be able to accept identification performed by another credit union.

Politically Exposed Persons

PEFP silhouette 1The proposed regulations have added new categories of Politically Exposed Persons (PEPs), as follows:

  • Close associates of Politically Exposed Foreign Persons (PEFPs)
  • Politically Exposed Domestic Persons (PEDPs), their family members and close associates
  • Heads of International Organizations (HIOs), their family members and close associates

Given that the list (contained in bill C-31) of qualifying positions for PEDPs includes mayors, it is likely that many if not most credit unions will have members classified as PEDPs. The draft regulations mitigate this somewhat by adding a prescribed period of 20 years to the definition of a PEDP.

Additionally, required measures for PEPs such as determining the source of funds, obtaining senior management authorization to keep an account open, and performing enhanced monitoring will only apply to PEDPs and HIOs (and their family members and close associates) who have been determined to be high risk. Despite these exceptions, identifying and documenting these new categories of PEP will add to credit unions’ compliance obligations.

Reasonable Measures

Many AML record keeping, reporting and determination requirements rely on “reasonable measures” to be taken by financial institutions. For example, in a Large Cash Transaction Report, certain information about the conductor of the transaction, such as their country of residence, their home and business telephone numbers are not mandatory, but reasonable efforts must be made to obtain the information, and if you have it on file, it must be included in the report. The proposed changes will mean that whenever you take “reasonable measures”, and the measures taken are unsuccessful, you will then need to keep a record describing what the measures were and the reason they were unsuccessful. This will require additional work and record keeping for categories such as FINTRAC reporting, PEP determinations and correspondent banking relationships, among others.

Public Comments

Public comments about the proposed changes will be accepted by the Ministry of Finance until September 4, 2015. They must be submitted in writing, as follows:

Mail       Attention: Lisa Pezzack

Director, Financial Systems Division

Department of Finance

90 Elgin Street

Ottawa, Ontario, K1A 0G5

Email: fcs-scf@fin.gc.ca

Need a Hand?

If you would like someone to look over your submission before you make comments to the Department of Finance, you can get in touch with us free of charge. We will look over your submission and make suggestions, without any cost to you. If you need a hand, please feel free to contact vCAMLO or Outlier.

Above And Beyond What?

It seems that every time I’m at a conference or event related to compliance, I hear people talking about going “above and beyond” the requirements. Something about this statement has always seemed wrong to me. It wasn’t until recently that I understood why: most of us aren’t getting the basics right.

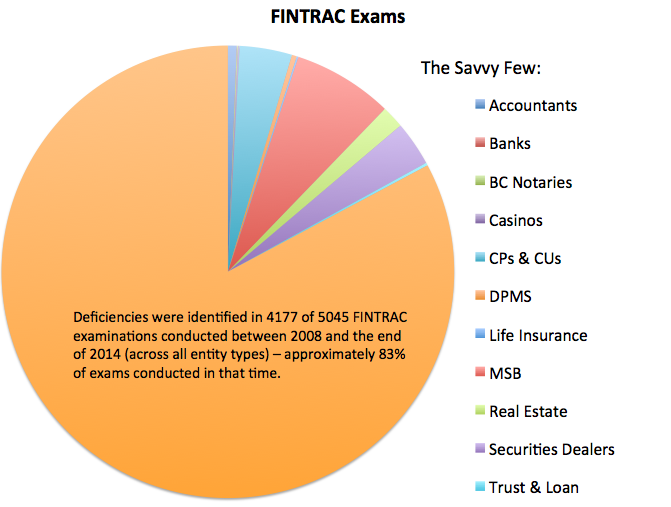
FINTRAC Examination Data


Most Of Us Are Failing At The Basics

This is not an indictment of Compliance Officers and the tremendous effort that goes into compliance. It’s a simple statistical fact.

We crunched some numbers by industry for anti-money laundering (AML) compliance in Canada based on information obtained from the regulator through an access to information request in 2014. The rate of examinations for which there were no deficiencies (across all reporting entity types) was 17 percent. While we congratulate the savvy few that met this bar, that leaves 83 percent of reporting entities that failed to meet the basic requirements in some way.

While these results are specific to examinations conducted by the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC), it’s not unreasonable to assume that the results can be generalized to compliance more broadly.

Shift The Focus

Before anyone can go “above and beyond” the fundamentals should be solid. One of the most painful reviews (like an audit for compliance) that I’ve conducted was a classic case of going above and beyond while completely missing the mark on baseline compliance. The reporting entity had great technology and related risk ranking metrics. The methods that they used to understand customer behavior involved machine learning and geo-location data at each login, analyzed over time. It was a great risk management strategy, except that they hadn’t identified a single customer in accordance with the law. Not a single one…

Ironically, in working to design measures that went beyond the basic compliance requirements, they found themselves so far outside of what was allowable under the law that had an examination been conducted by a regulator at the time, they could have been facing a very hefty penalty (as was the case for Ripple Labs in the USA).

Rework

Consequently, they spent a good deal of time and money updating their systems and identifying customers. In some cases, customers were lost. The (re)identification process was frustrating for people that believed that they had already completed everything that was needful in order to transact freely. There were updates to process documents and IT systems that took place over the course of months, and a good deal of frustration at the rework involved.

A competent third party or in house expert can be useful in assisting with system and process design, provided that they are able to understand your business model, basic compliance requirements and how to achieve these in the most elegant way possible.

Keep It Simple (Seriously)

At a recent conference, I was listening to a speaker whom I consider a model for what not to do, both functionally and ethically. As he sweepingly gestured towards an overly complex chart, he stared into the blank faces of his audience and proclaimed “It’s ok if you don’t get it. That’s not the point. The point is that I should look impressive. Are you impressed?” I was not.

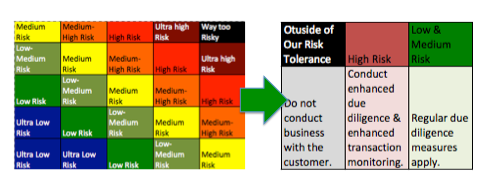
Which model fits your needs?

Which model fits your needs?

Remember that the people that are usually fulfilling your compliance requirements are your frontline staff. Would they be able to use the model to the left to risk rank your customers?

While it can be tempting to create complex rating systems, it’s important to understand that your compliance program should be functional. If the system that you’ve created is too complex for your staff to understand and adhere to, it will fail. Whether you’re hiring someone external or creating your program in-house, remember to keep it as simple and easy to follow as possible.

Ask, Check, Test

One of the many arguments that I’ve heard for going above and beyond is that this is helpful when dealing with regulators and banking service providers. While I agree that this can certainly be the case, it’s a moot point if the basic requirements are not met.

In my experience, both regulators and bankers are candid – when asked – about where their expectations are set. There is no real appetite on the part of either to create a set of secret standards related to going above and beyond. From a practical perspective, this means that reporting entities should be focused on understanding the basic requirements, and seeking clarification as needed.

Effectiveness reviews can also be a useful tool in this regard, provided that the reviewer or auditor is well versed in local compliance requirements. Similarly, internal testing should be geared towards baseline requirements to ensure that these are being met.

Opportunities & Innovation

Going above and beyond for its own sake (in terms of compliance) is neither required, nor particularly good business.

This is not to say that reporting entities should avoid innovation. Rather, these efforts should be focused and prioritized on finding the most cost-effective and efficient ways to meet baseline compliance requirements, and mitigating risk.

Changing compliance legislation can also provide opportunities for innovation, in particular where there are public consultations. This type of dialogue with lawmakers allows stakeholders to suggest alternatives that may mitigate risk in new and innovative ways. It provides an opportunity to showcase new technologies and processes that solve common compliance problems with greater efficiency (although they may not fit into the current regulatory paradigm).

Need A Hand?

We believe that good compliance is good business. If you have questions, please feel free to contact us.

Proposed PCMLTFR Updates

Screen Shot 2015-07-08 at 4.03.31 AM

We’ve created a marked-up version of the Proceeds of Crime (Money Laundering) and Terrorist Financing Regulations (PCMLTFR) that reflects the draft amendments posted in the Canada Gazette on July 4th, 2015.

Here’s a printable and downloadable PDF file: PCMLTFR Mark-Up (July 4, 2015 Draft Amendments)

If you would like a copy of the file in Microsoft Word, please contact us.

Need A Hand?

At Outlier, we believe that it is important to participate in decisions that affect you and your business.  If you would like someone to look over your submission before you make comments to the Department of Finance, you can get in touch with us free of charge.  We will look over your submission and make suggestions, without any cost to you.  If you need a hand, please feel free to contact us.

Unpublished FINTRAC Penalties

Jonathan Krumins, Vice President, vCAMLO

Today’s guest blogger is Jonathan Krumins, Vice-President, AML Risk & Compliance, at vCAMLO Solutions Inc. vCAMLO provides anti-money laundering (AML) and anti-terrorist financing (ATF) support to Canadian credit unions. You can learn more about vCAMLO at www.vcamlo.ca.

Background

Reporting entities (REs) often ask us about penalties, in particular when they are published publicly. Since 2009, The Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) has issued Administrative Monetary Penalties (AMPs) against persons and entities that were found to have violated the Proceeds of Crime (Money Laundering) and Terrorist Financing Act, and its associated Regulations. In many cases up to 2013, FINTRAC has published details on its website about each penalty, including the name of the person or entity, the dollar amount of the AMP, as well as the cited deficiencies. The AMP area of their website has two sections – a list of all published penalties, as well as a running total of AMPs imposed since December 30, 2008, divided by sector.

As of June 26, 2013, FINTRAC changed its policy regarding public notice of AMPs, so that they would be published if one or more of the following criteria are met:

  • The person or entity has committed a very serious violation; or
  • The base penalty amount is equal to or greater than $250,000, before adjustments are made in consideration of the person or entity’s compliance history and ability to pay; or
  • Repeat significant non-compliance on the part of the person or entity.

AMPs can only be published once the appeals process is exhausted, which can take years to complete. This process can include an appeal to FINTRAC’s director, and a subsequent appeal to the Canadian Federal court.

Understanding this context is vital for RE Compliance Officers. While trend information related to published and unpublished penalties is not likely of interest to frontline staff, understanding these patterns is useful in fielding questions from Senior Management and the Board of Directors.

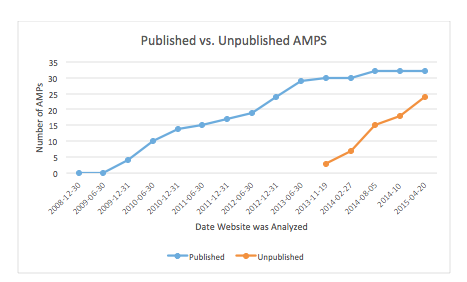
We have conducted an analysis of data published on the FINTRAC’s website which shows a trend of an increasing number of unpublished AMPs since 2013. These unpublished AMPs were primarily imposed on the Credit Union/Caisse Populaire and Money Service Business (MSB) sectors.

Methodology

We have made all calculations using information available as of April 20, 2015. We examined publicly available information on FINTRAC’s webpage, using the running total of AMPs by sector and the list of public AMPs. We also examined a summary of AMPs as of October 2014 obtained by Outlier through an Access to Information request. Our analysis focuses only on the sectors that have received AMPs, either published or unpublished: Credit Unions (including Caisses Populaires), MSBs, Real Estate Brokers, Securities Dealers and Casinos.

In addition, we accessed “cached” versions of FINTRAC’s website to review past versions in order to include six public AMPs that were issued between August 19, 2009 and April 26, 2010. In accordance with FINTRAC policy, these were removed from FINTRAC’s website after the five year public notice period had expired. We have included this historical data in order to provide a full view of the penalties issued. It is noteworthy that there are likely additional penalties in the process of being appealed (this information cannot be made available until the appeals process is complete).

Published AMPs vs. Unpublished AMPs

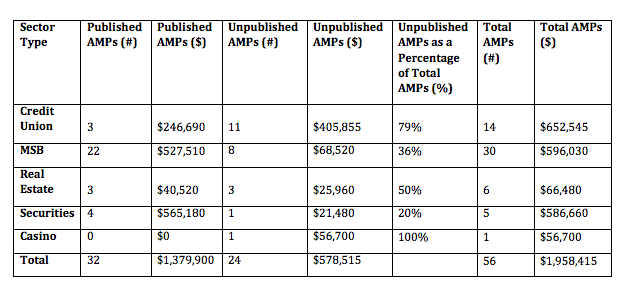
By analyzing the list of published penalties, compared to the running total of AMPs, it appears that there have been a significant number of unpublished penalties:

FINTRAC AMPs

Credit Unions

Credit Unions have received the largest number of unpublished penalties, both in terms of number and dollar amount. Credit unions have received 3 published AMPs, totalling $246,690. They have also received an additional 11 unpublished AMPs, totalling $405,855.

Trend analysis: This appears to be a significant increase in overall enforcement action by FINTRAC in the Credit Union sector. The total number of penalties against Credit Unions have increased sharply to 14, which means that Credit Unions now have the second largest number of listed AMPs (published and unpublished), behind MSBs. All penalties against Credit Unions since 2013 were unpublished. This data can also be interpreted to mean that FINTRAC’s enforcement efforts against Credit Unions have increased since 2013, however it is important to remember that AMPs are listed on FINTRAC’s website after they are finalized, which can mean a significant gap between when an AMP was issued and when it is listed, especially if there is an appeal involved.

Money Service Businesses (MSBs)

MSBs have received 22 published penalties, totalling $527,510. They also have received eight unpublished penalties, totalling $68,520. Interestingly, a $12,880 penalty that was published against an MSB on July 11, 2013 no longer appears on FINTRAC’s website.

Trend analysis: MSBs continue to be the leading sector in terms of receiving AMPs, although similar to the other sectors examined, the majority of AMPs that were against MSBs from late 2013 through to 2015 were unpublished.

Real Estate Brokers

Real Estate Brokers have received three published penalties totalling $40,520 compared to three unpublished penalties totalling $25,960.

Trend Analysis: Real Estate Brokers have received relatively few published and unpublished penalties in comparison to the Credit Union and MSB sectors. The number of unpublished penalties (compared to the number of published penalties) is consistent with trends across all sectors.

Securities Dealers

Securities Dealers have received four published penalties totalling $565,180 compared to one unpublished penalty of $21,480.

Trend Analysis: Securities Dealers have received relatively few published and unpublished penalties in comparison to the Credit Union and MSB sectors.

Casinos

Casinos have never received a published AMP, however FINTRAC’s website shows an unpublished AMP of $56,700 issued against a casino. This may be surprising to anyone that has read about BC Lottery Corporation, however, AMPs are not part of these records until the appeals process has been exhausted (and there have been successful appeals).

Trend analysis: It is difficult to establish a trend based on a single data point, however this unpublished AMP shows that the Casino sector is no longer unaffected by FINTRAC penalties.

What Does This All Mean?

Screen Shot 2015-05-06 at 11.58.01 AM

Note: The dates on the above graph represent when FINTRAC’s website was analyzed to calculate the total number of penalties, with the exception of October 2014, which is the “as of” date of an AMP listing received in a Freedom of Information request. Data for unpublished AMPs is only available since 2013.

As of June 2013, FINTRAC began to apply the updated standard for publicly listing AMPs. Since this change, unpublished penalties comprise approximately 42% of all issued AMPs by amount and 43% by number. While this is excellent news for REs that are concerned with the negative media and other reputational risk related to published penalties, it will make it more difficult to assess the reasons that REs are receiving penalties. The specific violations that led to a penalty are only made public by FINTRAC when the AMP is published. In order to ensure that our Credit Union clients are well-informed about industry trends related to penalties, vCAMLO will be requesting additional information and performing trend analysis. Stay tuned!

Your Best Defence

To avoid AMPs, it is essential to constantly test for weaknesses in your compliance regime. Conduct rigorous effectiveness testing (this is required at least every two years), and consider more frequent testing. Finally, ensure that immediate steps are taken to remediate deficiencies received in FINTRAC exams. Deficiencies that re-appear in follow-up exams are taken seriously by FINTRAC, and can lead to penalties, published or not.

Need a Hand?

vCAMLO: If you are a credit union or MSB, and have any questions related to financial compliance, or if you are interested in AML Support Services, please contact us for a complimentary 30 minute compliance discussion.

Outlier: If you need assistance reviewing your technology solution or FINTRAC reporting to be certain that you’re meeting the standard described in this blog, or just someone to chat with to make sure that you’re on the right track, please contact us.


Suspicious Transaction Reporting in 2015

Preparing for a FINTRAC examination

At the Canadian Institute’s 14th Annual AML Forum, the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) reviewed its expectations for suspicious transaction reporting. FINTRAC emphasized that suspicious transaction reports (STRs) are vital to the agency’s mandate as Canada’s financial intelligence unit (FIU) and ongoing collaboration with law enforcement agencies. While reporting entities (REs) in Canada have been required to report transactions for quite a few years, we’ve had many questions from REs about what FINTRAC expects and looks for in examinations. FINTRAC’s most recent guidance is useful in tuning your technology, enhancing your processes, and asking the right questions at industry association meetings.

What is FINTRAC Looking for in STRs?

When FINTRAC conducts compliance examinations, they will be applying three tests to STR data, including:

  1. Entity Practitioner: FINTRAC will look for transactions that are similar to those involved in STRs that you have reported. If there are similar transactions or transaction patterns that have not been reported to FINTRAC, there should be an explanation for the difference. Where possible, this explanation should be documented.
  2. Sector Practitioner: FINTRAC will compare the number and type of STRs submitted by similar entities. The size and type of business are taken into consideration.
  3. Reasonable Practitioner: FINTRAC will analyze a sample of reported STRs and unreported transactions against relevant guidance. In this case, relevant guidance means the suspicious transaction indicators from FINTRAC’s Guideline 2 that are applicable to your business.

These are terms that we’re likely to hear more about over the coming months, and there are compliance program adjustments (most of them relatively simple) that can be made to ensure that you’re meeting this standard.

Tune Your Technology

Amber looking at laptop FINTRAC screen

Most REs use software solutions to detect potentially suspicious transactions. Almost all transaction monitoring software uses some type of rules-based system to determine when alerts should be generated. These rules should, at minimum, reflect the indicators that are applicable to your business. Not all of the indicators from FINTRAC’s Guideline 2 will be applicable to your business. Where possible, you should document the decisions that you make about your transaction monitoring rules, including the rationale for those decisions.

The most sophisticated software platforms have machine learning functions. These can take the decisions that have been made about previous alerts and use this information to refine how the program works. For example, if a particular pattern of transactions was deemed to be suspicious, the program may look for similar patterns.

If you’re not using software that does this on its own, don’t panic. You can review the STRs that you’ve submitted to FINTRAC to determine whether your transaction monitoring rules are tuned to reflect the types of money laundering and terrorist financing threats that you’ve previously encountered. This should be done on a regular basis (for example, as part of your Risk Assessment updates). If you have an STR that is related to a pattern that you don’t have a rule to cover, you may want to do this sooner, rather than waiting for the next scheduled update.

Train Your Staff

Training

Over the years, I’ve heard many Compliance Officers express frustration about not knowing whether or not STR data has been useful to FINTRAC or law enforcement. To close this gap, I’ve looked for articles and speakers from FINTRAC and law enforcement that could provide meaningful information about the type of information that is most useful. The same principle applies to your staff.

You can use existing cases (you’ll want to remove any personal information for training purposes) to demonstrate the type of transactions that you want your staff to escalate to compliance for review. Existing cases from the media, and end to end cases provided by training companies like TAMLO, are also excellent resources. Keeping your annual training fresh is a challenge, and using your STRs as cases is one way to do that, while also meeting FINTRAC’s expectations.

Refine Your Audits & Effectiveness Reviews

AML Compliance Effectiveness Review

Are your auditors and/or reviewers using the same tests that FINTRAC is using to assess your compliance? If you’re not certain, ask.

If you perform self-assessment testing, you may want to include these tests as well.

As of 2015, all AML Compliance Effectiveness Reviews performed by Outlier will use these three key tests to assess STR data.

Ask Your Industry & Working Groups for More

Hanshake

Most REs have excellent industry associations and working groups such as the Canadian Banker’s Association (CBA), Canadian MSB Association (CMSBA) or the Canadian Jewellers Association (CJA). These groups are excellent resources and can help you understand STR trends across your industry. If you’re not a member, you may still be able to attend regular conferences or events.

Need A Hand?

We would love to hear from you. If there are topics that you would like to know more about, or if you need assistance with your compliance program, please contact us.

FINTRAC Examination Results for MSBs

The Canadian Money Services Business Association (CMSBA) recently held their Spring Training events in Montreal, Vancouver and Toronto.  The list of speakers included MSB industry professionals, as well as representatives from regulators including the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC).  For a full synopsis of the Montreal and Toronto events, click here.  FINTRAC presented excellent statistical data about how MSBs have fared in examinations conducted between April 2011 and July 2014.  So how are MSBs faring?  Very well overall. 
ZDE FINTRAC 2008-2013

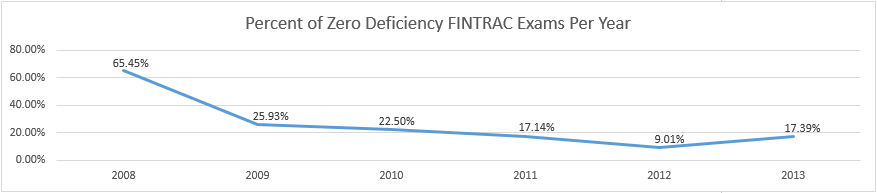
Data obtained through a freedom of information request indicates that almost 25% of MSBs examined between 2008 and 2013 have not had any deficiencies.

How Does FINTRAC Decide Who Is Examined?

FINTRAC considers several factors when deciding which reporting entities (REs) will be examined.

  • Concurrent Examinations: examinations conducted in tandem with the Office of the Superintendent of Financial Institutions (OSFI). This is applicable to federally regulated financial entities (FRFEs) like banks.
  • Market Share: The largest reporting entities in Canada (because the larger an organization is, the more critical the risk of non-compliance will be);
  • Cyclical: Coverage of a whole industry (this seemed to apply most to Casinos).
  • Follow-Up: Subsequent examinations based, with an emphasis on the resolution of deficiencies found in previous examination(s) to ensure remediation. FINTRAC noted that although it is no longer a requirement to submit a formal action plan to FINTRAC, it is a best practice for REs to document (and update) an action plan internally.
  • Risk: FINTRAC’s evaluation of the RE’s risk, based on a broad selection criteria, such as money laundering and terrorist financing vulnerabilities, the likelihood of non-compliance and industry trends.
  • Theme-Based: Related to specific intelligence about a RE or type of business that indicates there may be an elevated risk of non-compliance, money laundering vulnerability or terrorist financing vulnerability.

Methodology & Analysis

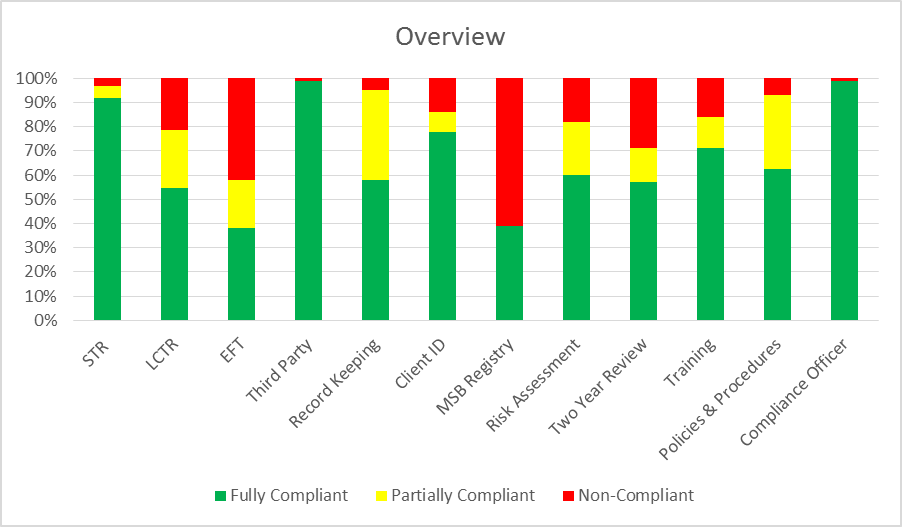
FINTRAC’s statistical analysis of MSB adherence to the requirements laid out in the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA) and its regulations is broken down by percentage, the results of the exams conducted that were fully compliant, partially compliant and non-compliant.  These are colour coded:

  • Green: fully compliant (no deficiencies were observed),
  • Yellow: partially compliant (there was something in place, but the MSB missed something), and
  • Red: non-compliant (in most cases, there was nothing in place or a reporting timeframe was missed).

Overall examination results have been positive.
Overview

It’s noteworthy that if FINTRAC has, as of 2014, found something during an examination that is considered ‘immaterial’, it’s not cited.  For example, in a large sample, if there are two client addresses that appear to be PO boxes, but all other client addresses were complete and in acceptable formats, there may not be a citation.  In these cases, FINTRAC may inform the RE verbally, but it will not be part of the formal ‘findings’ letter.

Compliance Officer

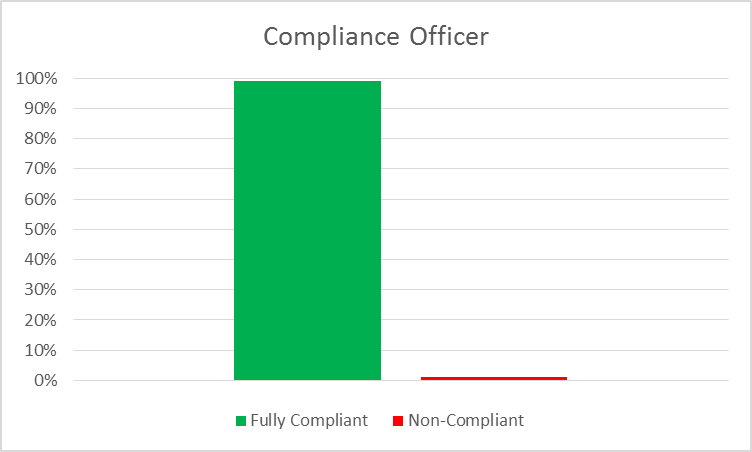
MSBs are required to have a Compliance Officer (a person that is responsible for overseeing the AML & ATF compliance program).  The appointment of the Compliance Officer must be documented in writing.  FINTRAC staff chided that this is likely the easiest area to achieve a fully compliant result in examinations.  MSB examination results certainly reflected this.
CO Chart

From a total of 612 MSB examinations considered, 608 MSBs were fully compliant.

Only four MSBs were deemed to be non-compliant.  It was noted that these were generally new market entrants that did not appear to understand Canadian AML & ATF compliance requirements.

Policies and Procedures

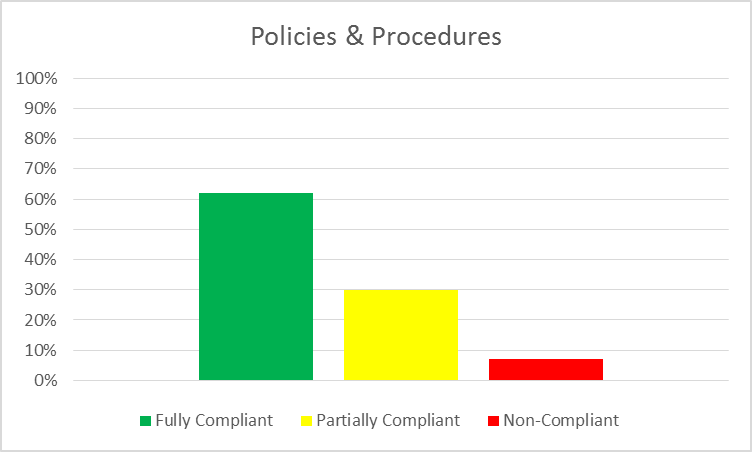
MSBs are required to have policies and procedures.  Policies describe the MSB’s regulatory obligations, while procedures describe what the MSB is doing to meet those requirements.  These must be documented, in writing, and the procedures must cover both staff and agents (if the MSB has agents).
PP Chart

From a total of 765 MSB examinations considered, 477 MSBs were fully compliant.

In 230 examinations, MSBs were deemed to be partially compliant.  Common errors included:

  • The omission of the 24-hour rule (specific descriptions of how the MSB determined whether or not reportable transactions had occurred over a 24 hour period),
  • Third party determinations (specific descriptions of when an MSB must determine if there is a third party involved, as well as what information needs to be collected and recorded), and
  • Politically exposed foreign person (PEFP) determinations (specific descriptions of when an MSB must determine if their client is a PEFP, and if so, what information needs to be collected/recorded. There is also a requirement that senior management signoff on the account within 30 days of the determination).

A total of 55 MSBs did not have any documented policies or procedures. In some cases, FINTRAC noted that there appeared to be processes in place, but that these were not documented in writing.

Training

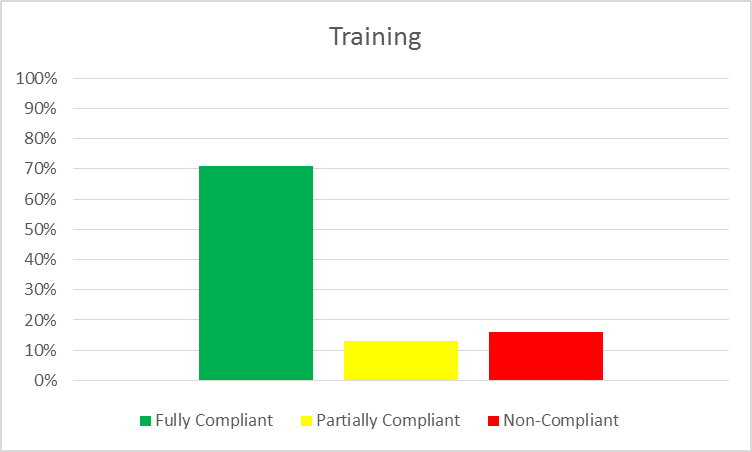
MSBs are required to have an ongoing training program. The training program must be documented (who, what, where, when and how) and delivered to all staff and agents on an annual basis, at minimum.
Training Chart

From a total of 487 MSB examinations considered, 346 were fully compliant.

In 63 examinations, MSBs were deemed to be partially compliant.  Common errors included:

  • Interviews conducted with staff during an examination that evidenced a misunderstanding of the requirements (during an exam, FINTRAC will interview random staff members related to regulatory requirements to ensure training effectiveness)

In 78 examinations, MSBs did not have any training in place, or if they did, it was not documented.

Among the training options available to MSBs, we’re most excited about a relatively new offering from TAMLO that includes fast paced and visually stunning video content, as well as testing and tracking tools for Compliance Officers.

AML Compliance Effectiveness Review

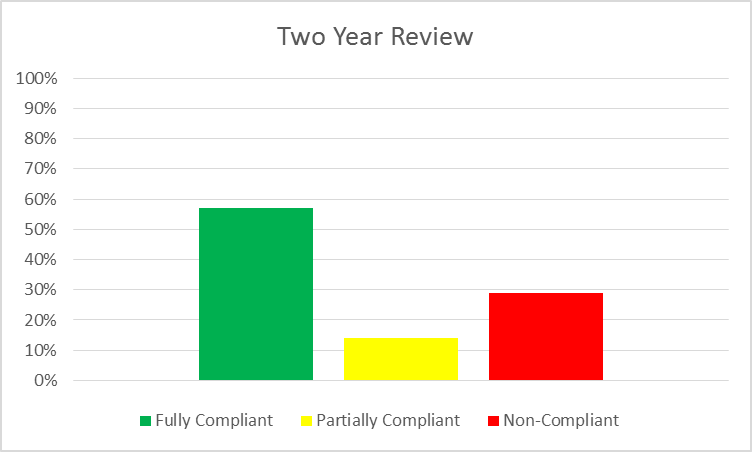
MSBs are required to complete an AML Compliance Effectiveness Review once every two years.  The review must cover all policy and procedure documentation, as well as operational testing to ensure procedures are being properly followed.
2YR Chart

From a total of 722 MSB examinations considered, 412 were fully compliant.

In 101 examinations, MSBs were deemed to be partially compliant.  Where MSBs missed the mark was typically because they did not respect the two year cycle.  Other common errors included:

  • Only reviewing the policy documents with no operational testing of whether they are being followed (the policy document tells staff and agents what to do. Procedures tell them how to do it.  MSBs must be sure they are testing whether staff and agents are adhering to the procedures).

In 209 examinations, MSBs had not conducted an effectiveness review or could not provide evidence of one taking place.

Risk Assessment

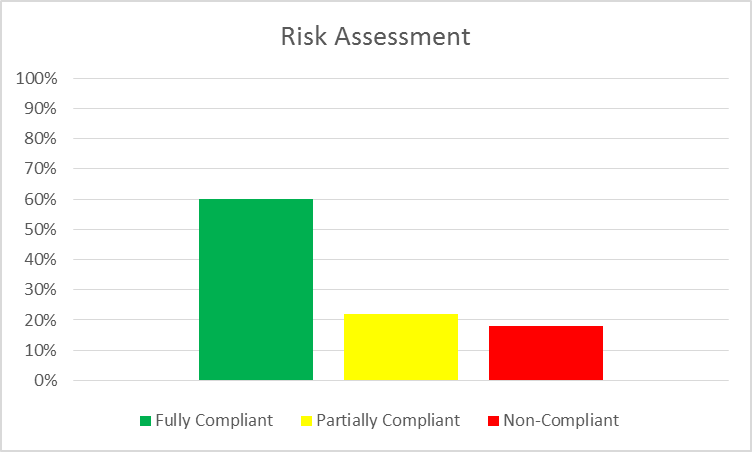
MSBs are required to assess the risk that their business could be used for money laundering or terrorist financing.  The risk assessment must include four key components:

  • Products, services and delivery channels;
  • Geography;
  • Customers; and
  • Any other relevant factors.

Risk must be assessed and scored, and mitigated by appropriate controls.
RA Chart

From a total of 720 MSB examinations considered, 432 were fully compliant.

In 158 examinations, MSBs were deemed to be partially compliant.  The main issue was failing to include one of the four required elements. In some cases, a risk assessment was in place, but the documentation was not sufficient in assessing the MSB’s risk and controls.

In 129 examinations, MSBs had no evidence of a risk assessment.

FINTRAC noted that additional industry-specific risk assessment guidance is expected to be published later this year.

MSB Registration

MSBs are required to register with FINTRAC, as well as update their information within 30 days if there are any changes to business activities, banking or agent information.
MSB Reg Chart

From a total of 591 MSB examinations considered, 230 were fully compliant.

In this category, no partially compliant ratings were provided (the MSB registration was either complete, accurate and up to date, or it was deemed to be non-compliant).

In 361 examinations, MSBs were deemed to be non-compliant.  Most issues were due to a failure to update information when something within the business had changed or a failure to list all business activities. For example, the MSB registration may indicate that an MSB only performed foreign exchange in a case where remittance services were also provided.

Client Identification

MSBs are required to identify their clients in certain situations.  There are prescribed methods for completing this both in person and non-face-to-face (NF2F), and the identification document (ID) information must be recorded.
Client ID Chart

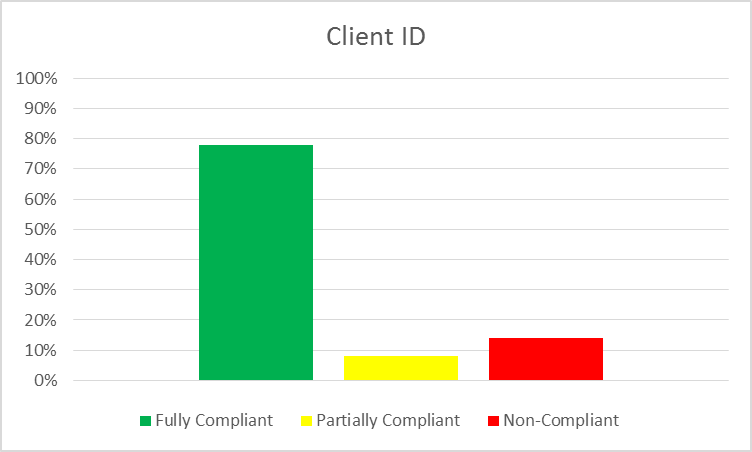
From a total of 796 MSB examinations considered, 621 were fully compliant.

In 64 examinations, MSBs were deemed to be partially compliant.  Common errors included:

  • Unacceptable ID (such as health card in Ontario);
  • Accepting ID that was expired at the time of the transaction (identification documents must be valid, or not expired, at the time they are reviewed);
  • Failing to record the prescribed details of the ID used (when reviewing a client’s ID, MSBs must keep a record of certain prescribed information); and
  • In Non-Face-To-Face Identification situations, only using one method, or using an unacceptable combination of methods (when identifying a customer who is not physically present, there are prescribed methods of how this is to be accomplished).

In 111 examinations, MSBs were non-compliant with client identification requirements.

Record Keeping

MSBs are required to keep certain records related to transactions and client identification.  These records must be stored in a manner that they can be accessed in the event they are requested, and must be maintained for at least five years.
RK Chart

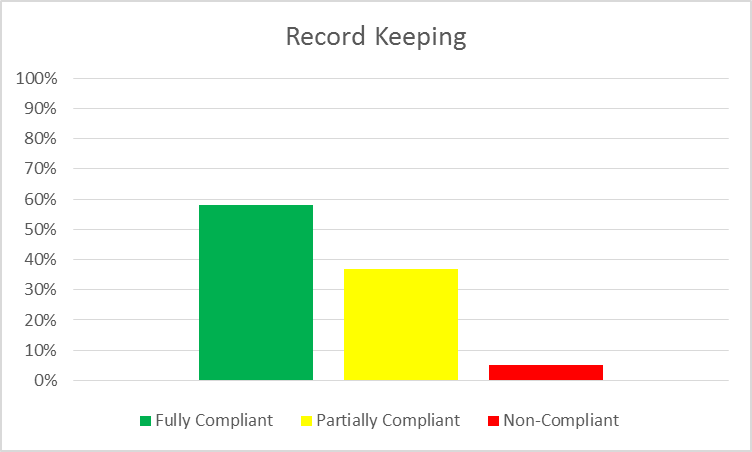
From a total of 811 MSB examinations considered, 470 were fully compliant.

In 300 examinations MSBs were deemed to be partially compliant.  In these cases, record keeping was taking place but elements of the record keeping requirements were being overlooked.  Common issues included:

  • Missing telephone numbers;
  • Vague occupation information (for example “manager” or “worker”);
  • PO boxes recorded as customer addresses;
  • Missing postal codes;
  • Third party determinations that were incomplete; and
  • Payment methods for incoming and outgoing payments.

In 41 examinations, MSBs were non-compliant with record keeping requirements.

Third Party Determinations

MSBs are required to make a third party determination in certain prescribed circumstances, as well as collect and record certain information (name, address, date of birth, occupation and relationship to your client) about the third party.

TPD Chart

The total number of MSBs included in the review was not provided, with the statement: “there was not enough information available to conduct reasonable analysis”.  However, the total number of non-compliant MSBs was 6, indicating that approximately 600 MSB examinations were considered in this sample.

FINTRAC Reporting

When FINTRAC assesses reporting obligations, it uses the internal acronym “QTV”, which stands for quality, timing and volume.  Quality refers to the information in the report, specifically, if the report has all the required information.  Timing simply means, was the report filed within the designated timeframe.  Volume is slightly more complicated, but mainly refers to the amount of reports you have filed compared to your previous submissions.  It was noted that typically, where MSBs were deemed partially compliant, it was due to the quality.  Where non-compliance was related to the timing.

Electronic Fund Transfers Reports

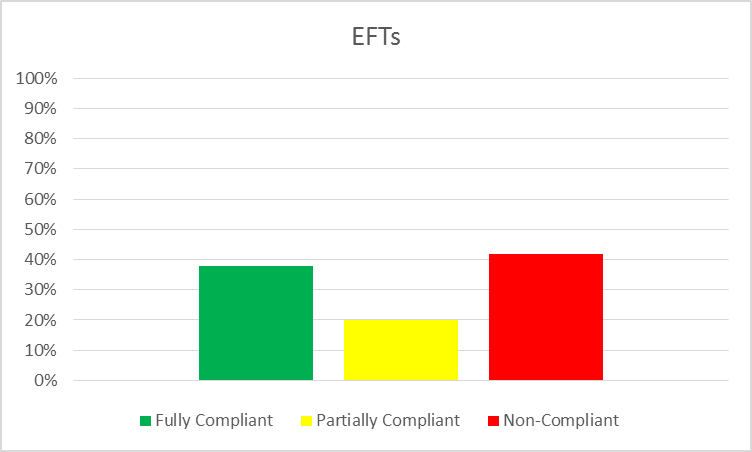
MSBs are required to submit electronic funds transfer (EFT) reports to FINTRAC within 5 business days from the date the transaction took place.  An EFT includes the international transfer of CAD 10,000 or more, either in a single transaction, or multiple transactions within a 24-hour period.
EFT Chart

From a total of 434 MSB examinations considered, 165 were fully compliant.

In 87 examinations, MSBs were deemed to be partially compliant. MSBs were typically failing to include all required information, such as:

  • Phone number;
  • Date of birth; or
  • Postal code.

It is noteworthy that while not all fields are marked as required in F2R, all fields must be filled in if the MSB has recorded the information.

In 182 examinations, MSBs were deemed non-compliant, with most not reporting the EFTs within the specified time frame, and a small portion missing EFT reports.

Large Cash Transaction Reports

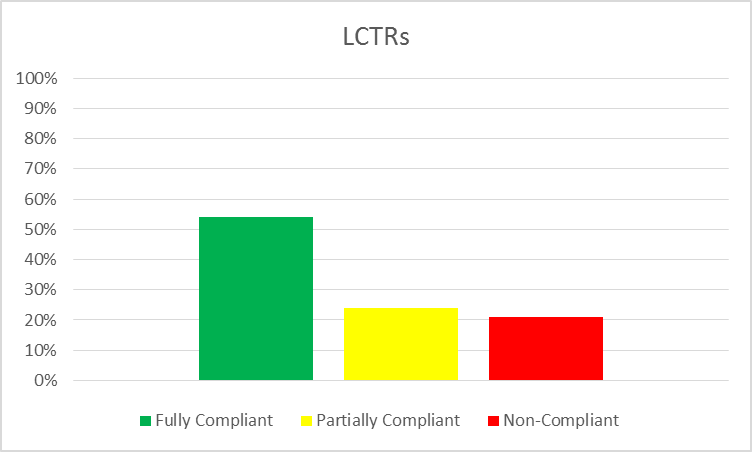
MSBs are required to submit large cash transaction (LCT) reports to FINTRAC within 15 calendar days from the date of the transaction, if the transaction was CAD 10,000 or more in cash, either in a single transaction, or multiple transactions within a 24-hour period.
LCTR Chart

From a total of 428 MSB examinations considered, 232 were fully compliant.

In 104 examinations, MSBs were deemed to be partially compliant.  MSBs were typically failing to include all required information, such as:

  • Occupation;
  • Date of birth;
  • Postal code; or
  • Type of ID used to identify the client.

In 92 examinations, MSBs were non-compliant, with most not reporting the LCTs within the specified time frame, and a small portion missing LCT reports.

Suspicious Transaction Reports

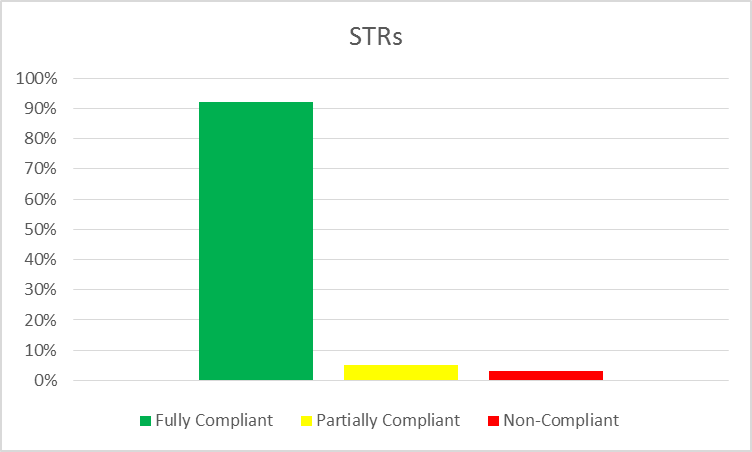
MSBs are required to submit suspicious transaction reports (STRs) and attempted suspicious transaction reports (ASTRs) to FINTRAC within 30 calendar days from the date the transaction is deemed suspicious by the Compliance Officer.
STR Chart

From a total of 285 MSB examinations considered, 262 were fully compliant.

In 14 examinations, MSBs were deemed to be partially compliant.  In these cases, MSBs were typically failing to include all required information.

In 9 examinations, MSBs were non-compliant.  Failing to file STRs carries relatively sever penalties, as the Canadian intelligence community relies on this type of reporting to build cases.  Where items are escalated as being potentially suspicious (either by staff or a transaction monitoring system), MSBs should always document the reason that these items are deemed not to be suspicious if no STR or ASTR reporting is completed.

Need a Hand?

If you are an MSB that needs compliance assistance (or a bank that wants assistance in setting up and maintaining a compliance regime that effectively manages MSB related risk), please contact us.


Return to Blog Listing